
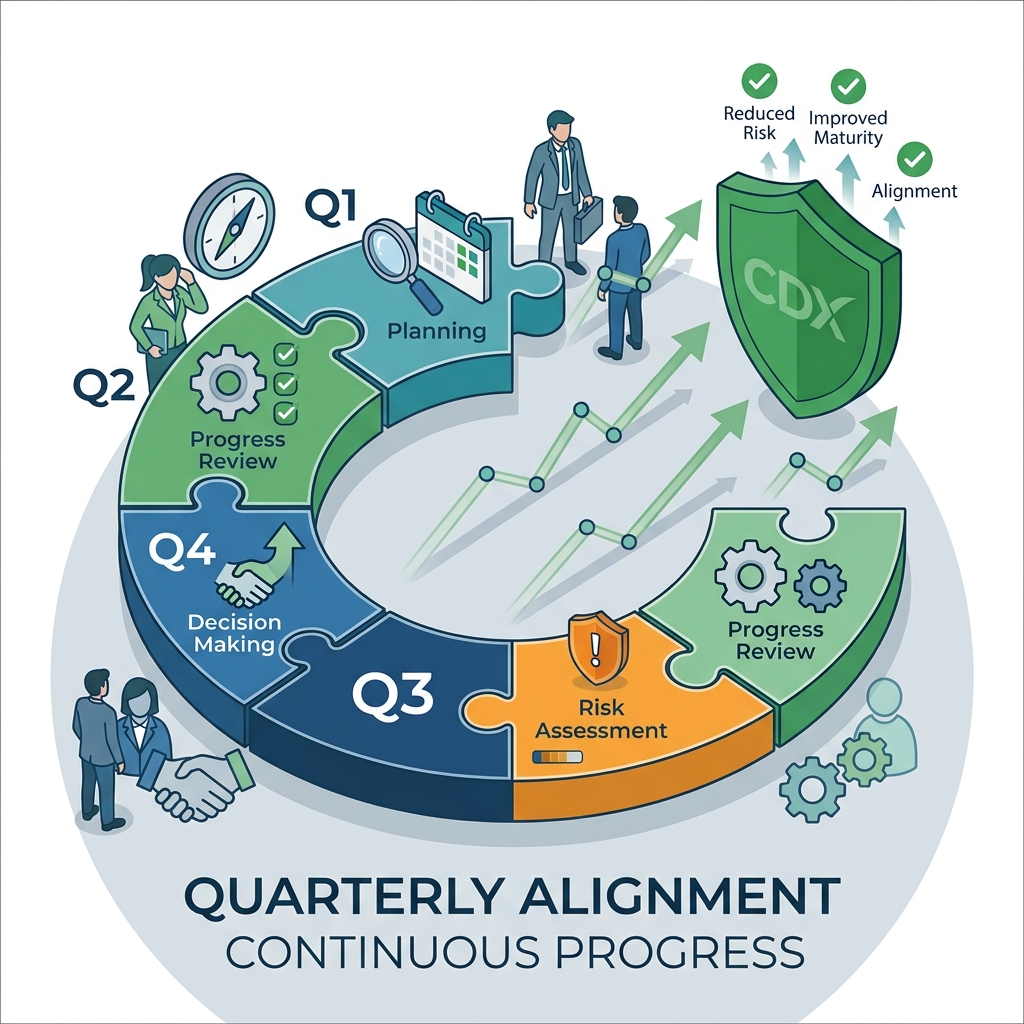
Cybersecurity is not a one‑time project — it’s an ongoing discipline. Organizations that treat cybersecurity as an annual activity often fall behind, lose momentum, and struggle to maintain alignment.
Quarterly cyber check‑ins solve this problem.
These short, structured sessions keep leadership, IT, and security aligned on priorities, progress, and emerging risks.
Why Quarterly Check‑Ins Matter
Quarterly check‑ins:
- Maintain momentum
- Reinforce accountability
- Keep priorities visible
- Support leadership engagement
- Highlight progress
- Identify new risks
- Strengthen communication
They ensure cybersecurity stays on the organizational radar.
How CyberDynamX Uses Quarterly Check‑Ins
Tier 3 of the CyberDynamX Assessment Program includes quarterly check‑ins (up to 30 minutes each). These sessions:
- Review progress on NOW / NEXT / LATER items
- Discuss changes in risk
- Clarify recommendations
- Support leadership decision‑making
- Maintain alignment
- Strengthen governance
They are short, focused, and highly effective.
Why Quarterly Works Better Than Annual
Annual reviews often:
- Miss emerging risks
- Overwhelm leadership
- Delay improvements
- Create large gaps
- Reduce accountability
Quarterly reviews keep cybersecurity proactive.
The Result
Organizations gain:
- Better alignment
- Faster progress
- Stronger governance
- Higher maturity
- Reduced risk
Quarterly check‑ins turn cybersecurity into a continuous practice.
Get The Assessment
