
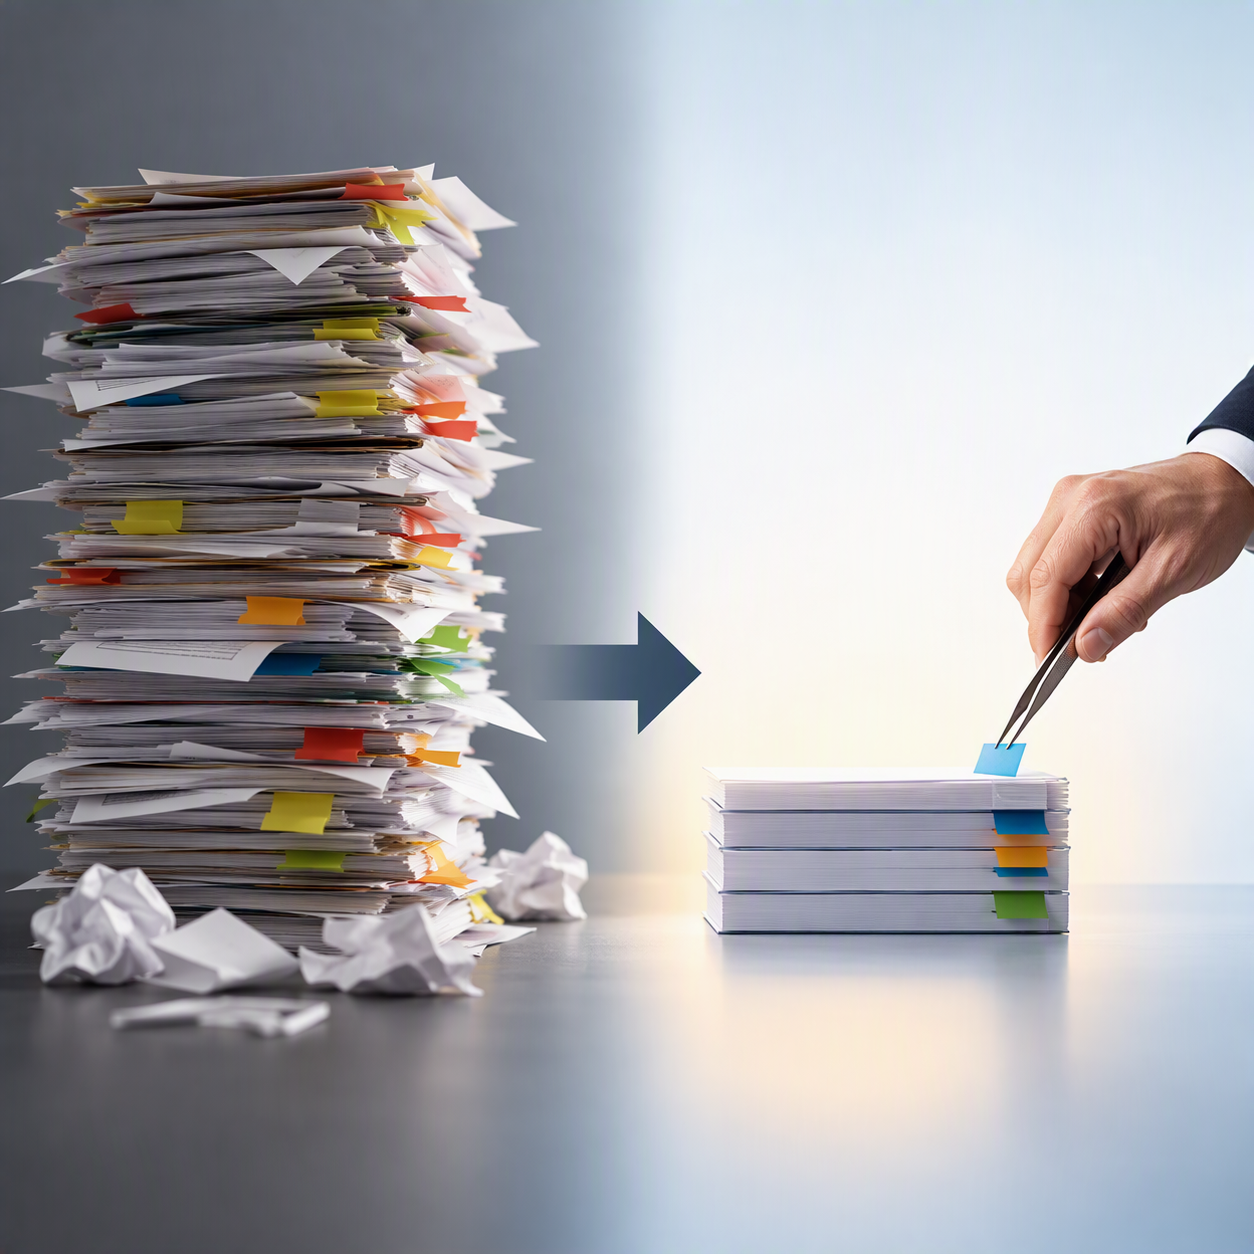
Many organizations assume that better cybersecurity governance requires more documentation. They create extensive policy libraries, multiple layers of standards, and a growing collection of procedures. Yet despite the effort invested, they often discover that employees do not read the documents, managers struggle to maintain them, and auditors find inconsistencies across the governance framework.
The reality is that over-documentation can become a risk in itself.
When governance artifacts multiply beyond what an organization can realistically use and maintain, confusion begins to replace clarity. Teams become uncertain about which requirements apply, implementation slows, and governance activities gradually become administrative exercises rather than meaningful risk management practices.
At CyberDynamX, we take a different approach.
Rather than producing documentation for documentation’s sake, our Governance Enablement Program applies a surgical methodology that focuses only on the governance elements that create measurable value. Every policy, standard, procedure, and baseline serves a specific purpose: improving clarity, reducing risk, supporting compliance, and enabling operational effectiveness.
Why Over-Documentation Fails
Organizations rarely struggle because they lack documentation. More often, they struggle because they have too much of it.
Excessive documentation can overwhelm staff, create conflicting guidance, and make implementation unnecessarily difficult. As more documents are added, governance becomes harder to communicate, maintain, and enforce. Audit activities become more complex because evidence, requirements, and responsibilities are spread across numerous artifacts.
The result is often governance fatigue. Teams spend their time navigating documentation rather than applying it.
Simply put, more documentation does not automatically create better governance.
The CyberDynamX Surgical Approach
Effective governance is built on relevance, not volume. Our approach emphasizes the documentation and controls that matter most to the organization’s objectives, risks, and compliance requirements.
This typically includes:
- Essential policies that establish direction and accountability
- Targeted standards that define required practices
- Practical procedures that support execution
- Actionable baselines that guide implementation
- Clear guidance tailored to business needs
- Integrated governance architecture that eliminates redundancy
Every component is designed to work together as part of a cohesive system rather than a collection of disconnected documents. The result is governance that remains powerful, manageable, and sustainable over time.
Why This Approach Works
Organizations are far more likely to adopt governance that is concise, practical, and clearly aligned to their day-to-day operations.
A streamlined governance framework is easier to communicate, easier to maintain, and easier to audit. Because requirements are clear and focused, leaders can enforce them with confidence, while teams can understand and apply them more consistently.
This approach also supports long-term maturity growth. Rather than constantly adding new documents to solve emerging challenges, organizations build a governance foundation that can evolve strategically as their needs change.
The outcome is greater clarity, stronger accountability, and less organizational friction.
The Result
Organizations that embrace a focused governance model gain more than just a cleaner document library. They establish governance that people can understand, follow, and maintain.
The benefits are straightforward:
- Stronger governance outcomes
- Better organizational alignment
- Reduced operational friction
- Higher governance maturity
- Sustainable, maintainable documentation
When governance is targeted, purposeful, and aligned to organizational realities, less truly becomes more.
Check out the Governance Enablement offering.
