
One of the greatest challenges in cybersecurity is not identifying problems. It’s deciding which problems to solve first.
Most organizations face dozens, if not hundreds, of competing priorities. Vulnerabilities need remediation. Policies require updates. Security tools need enhancement. Governance gaps need attention. Budgets are limited. Time is limited. Resources are limited.
When every issue appears important, decision-making often slows down.
Teams debate priorities. Leaders struggle to understand the relative impact of risks. Improvement initiatives compete for attention. As a result, organizations can spend significant time discussing what to do next instead of actually making progress.
The challenge is rarely a lack of information.
The challenge is a lack of clarity.
The Problem With Traditional Cyber Prioritization
Many cybersecurity programs generate large volumes of data. Assessments produce maturity scores. Security tools generate alerts. Audits identify findings. Consultants create reports. Governance reviews uncover recommendations.
While each of these outputs provides value, they are often presented separately.
Leaders are left trying to connect scattered pieces of information into a coherent picture of organizational risk. Different teams may interpret priorities differently, leading to conflicting viewpoints and inconsistent investment decisions.
Without a common framework for prioritization, cybersecurity can become driven by urgency, opinion, or the loudest voice in the room.
This creates friction, delays decision-making, and makes it more difficult to demonstrate meaningful progress.
Creating a Single View of Risk
The CyberDynamX Matrix was designed to address this problem.
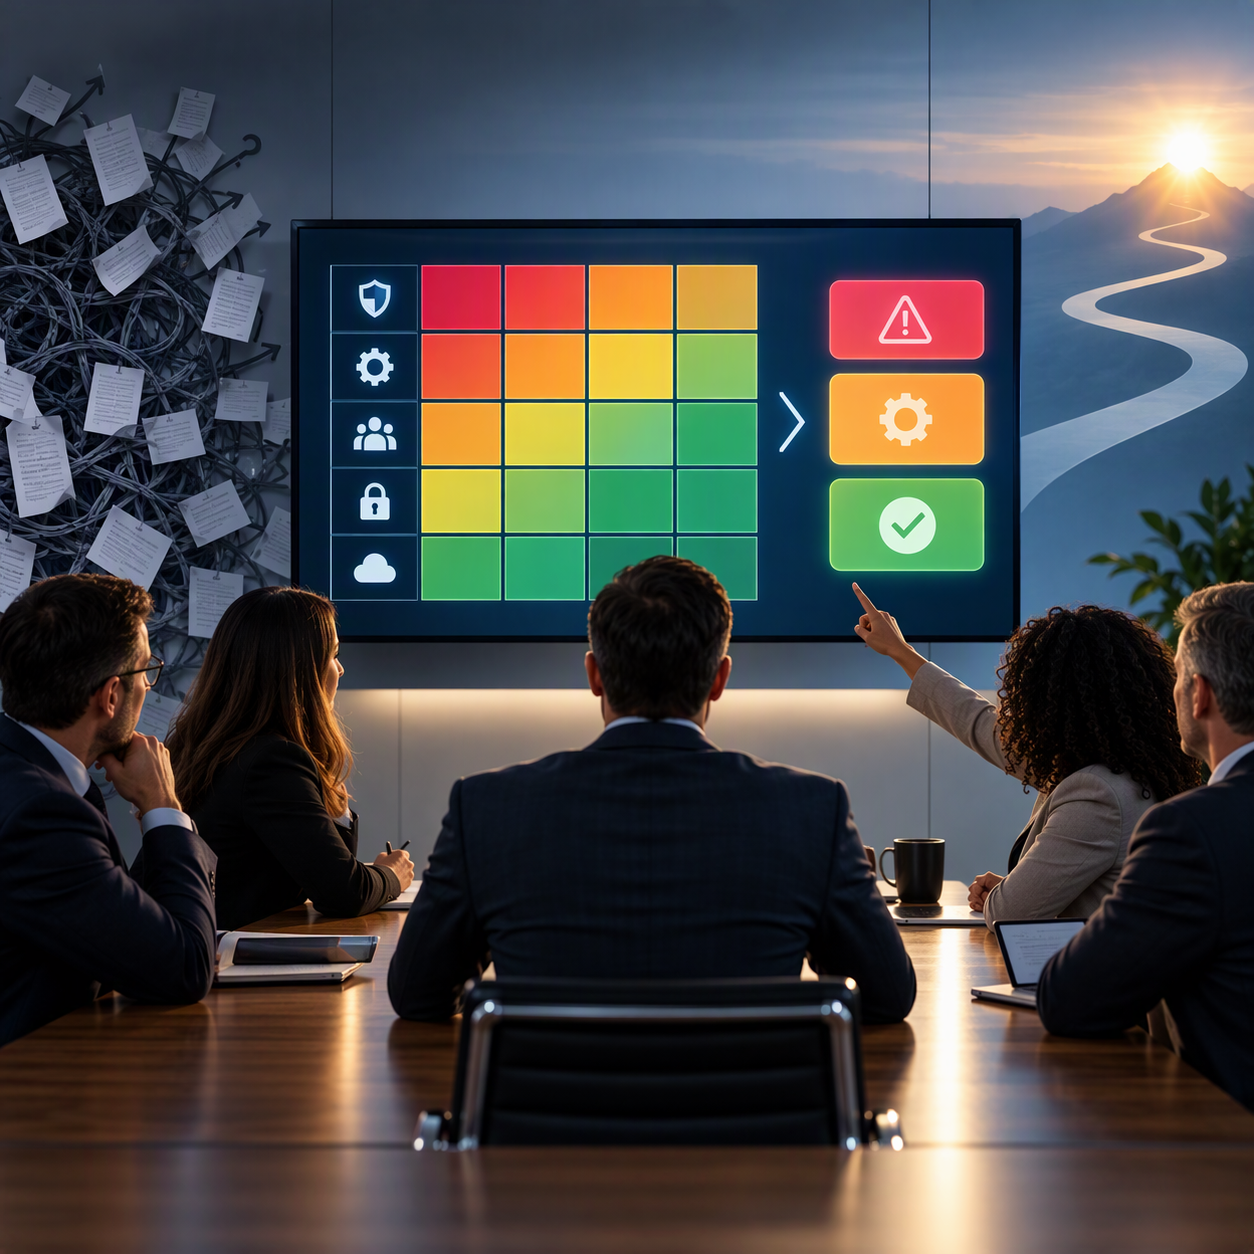
Rather than presenting cybersecurity information across multiple reports, dashboards, and spreadsheets, the Matrix provides a consolidated view of the organization’s cyber maturity and risk landscape on a single page.
By visualizing gaps, maturity levels, and risk exposure together, the Matrix helps leaders quickly understand where attention is needed most. Complex cybersecurity information becomes easier to interpret, discuss, and act upon.
Most importantly, the conversation shifts from “What do we think is important?” to “What does the evidence tell us is important?”
That shift fundamentally changes how organizations make decisions.
How the Matrix Improves Decision-Making
Effective decision-making depends on having both context and prioritization.
The CyberDynamX Matrix highlights the most significant gaps and organizes them into practical categories such as immediate priorities, near-term initiatives, and future improvements. This creates a structured path forward that leadership teams can understand and support.
Because the Matrix aligns findings across all NIST CSF functions, organizations gain a comprehensive view of cybersecurity maturity rather than focusing on isolated issues. Leaders can see how individual improvements contribute to broader organizational objectives and risk reduction efforts.
This shared view creates a common language for cybersecurity discussions. Technical teams, executives, governance committees, and business leaders can all reference the same information when making decisions.
As a result, conversations become more productive, priorities become clearer, and approval processes move more quickly.
Why Leaders Respond Well to Visual Prioritization
Cybersecurity is often perceived as complex because it is communicated in technical terms.
Leaders do not need more technical details. They need clarity.
A well-designed visual model allows decision-makers to see relationships, understand context, and evaluate priorities much more quickly than reviewing lengthy reports. When risk is displayed visually and tied to organizational objectives, leaders can make informed decisions with greater confidence.
This is one reason visual management tools have become so effective across many business disciplines. When complexity is simplified without losing accuracy, decision-making becomes faster and more strategic.
The Matrix applies that same principle to cybersecurity.
Rather than overwhelming leadership with data, it creates a concise and defensible framework for action.
Turning Information Into Action
Cybersecurity programs succeed when organizations can consistently convert information into decisions and decisions into action.
The Matrix helps bridge that gap by providing a practical mechanism for prioritization, communication, and governance. Instead of debating what matters most, organizations can focus on implementing improvements that have the greatest impact on risk reduction and maturity growth.
This enables faster progress while strengthening alignment between cybersecurity initiatives and business objectives.
The Result
Organizations that use a structured prioritization model gain faster decision-making, stronger governance, clearer communication, and better alignment between risk and investment decisions.
They spend less time debating priorities and more time improving security outcomes.
Ultimately, the value of the Matrix is not that it visualizes cybersecurity information.
Its value is that it enables better decisions.
And better decisions are what drive stronger cybersecurity, reduced risk, and higher organizational maturity.
Get the Matrix in The Assessment
