
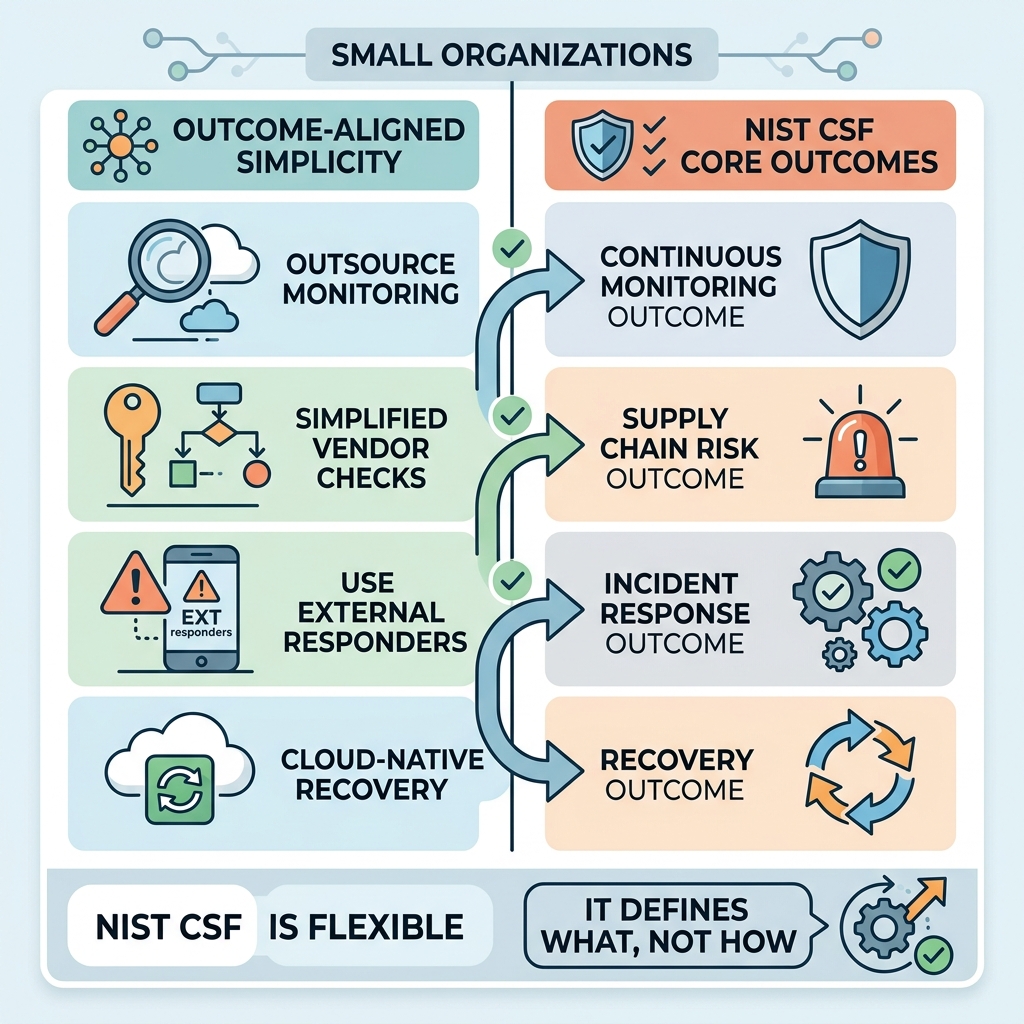
Small organizations often say, “That part of NIST CSF doesn’t apply to us.” But when you examine the outcomes, every one of them applies — even if the implementation looks different.
For example:
- Continuous Monitoring (DE.CM) Small organizations may outsource monitoring instead of building a SOC.
- Supply Chain Risk (GV.SC) Small organizations may use simplified vendor questionnaires instead of enterprise‑level assessments.
- Incident Response (RS.MA, RS.MI) Small organizations may rely on external responders instead of internal teams.
- Recovery (RC.RP) Small organizations may use cloud‑native recovery instead of custom-built infrastructure.
The outcome is the same. The method is different.
NIST CSF is flexible by design. It defines what must be true — not how you must achieve it.
Small organizations don’t need enterprise‑level complexity. They need outcome‑aligned simplicity.
Get The Assessment here: The Assessment
