
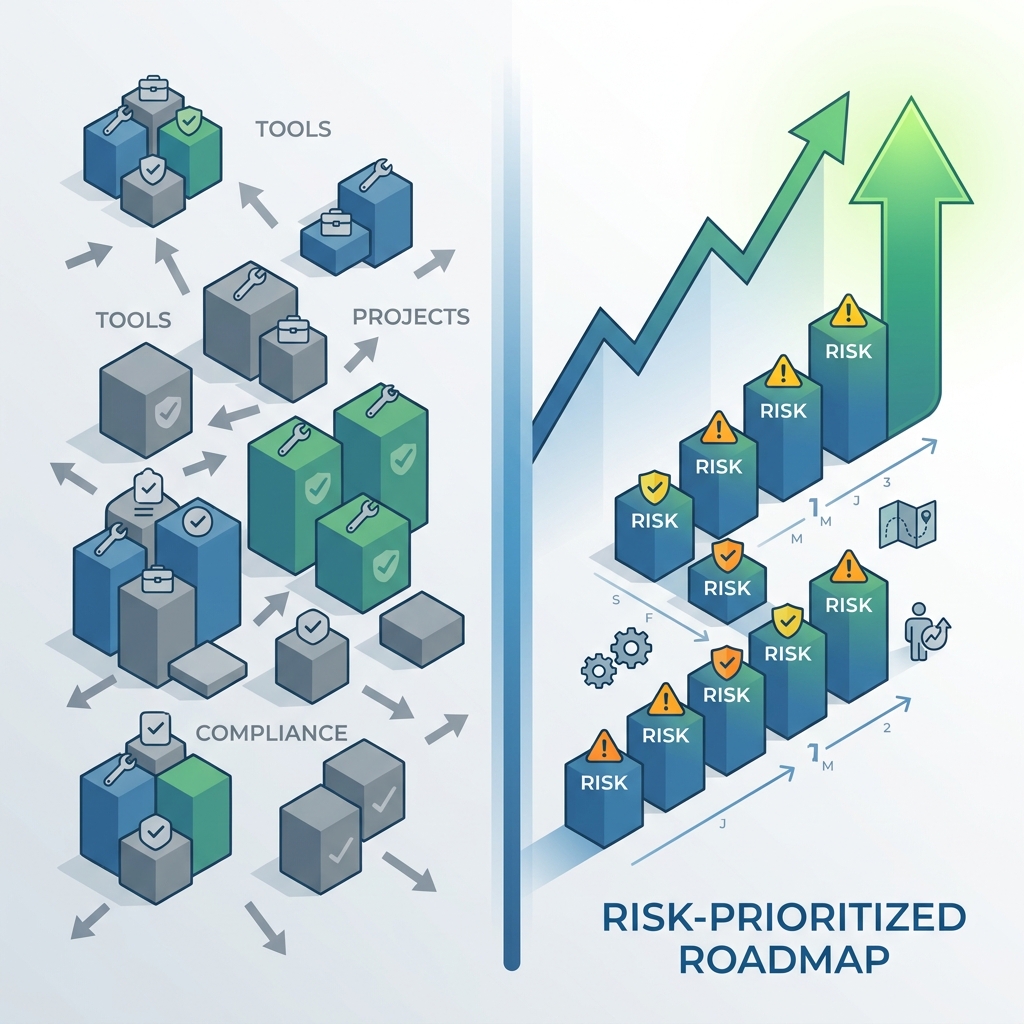
Cybersecurity roadmaps are often created based on tools, projects, or compliance requirements — not risk. This leads to misaligned priorities, wasted resources, and slow maturity growth.
Risk‑prioritized roadmaps solve this problem.
They align cybersecurity improvements with the organization’s highest‑risk gaps, ensuring resources are used where they matter most.
Why Roadmaps Matter
Roadmaps:
- Provide structure
- Support planning
- Align teams
- Guide investment
- Strengthen governance
- Accelerate maturity
But only if they are risk‑based.
How CyberDynamX Builds Risk‑Based Roadmaps
Tier 3 of the CyberDynamX Assessment Program includes a risk‑based cybersecurity roadmap that:
- Focuses on the 10–15 lowest‑scoring subcategories
- Provides a two‑year timeline
- Includes person‑effort estimates
- Outlines high‑level improvement steps
- Aligns improvements with maturity goals
- Supports leadership decision‑making
This turns prioritization into action.
Why Risk‑Based Roadmaps Work Better
Risk‑based roadmaps:
- Reduce exposure faster
- Improve resource allocation
- Strengthen alignment
- Support governance
- Increase maturity
- Build resilience
They ensure cybersecurity grows in the right direction.
The Result
Organizations gain:
- Faster maturity growth
- Better alignment
- Stronger governance
- Reduced risk
- Clear direction
Roadmaps turn strategy into progress.
Get the visibility you need: The Assessment
