
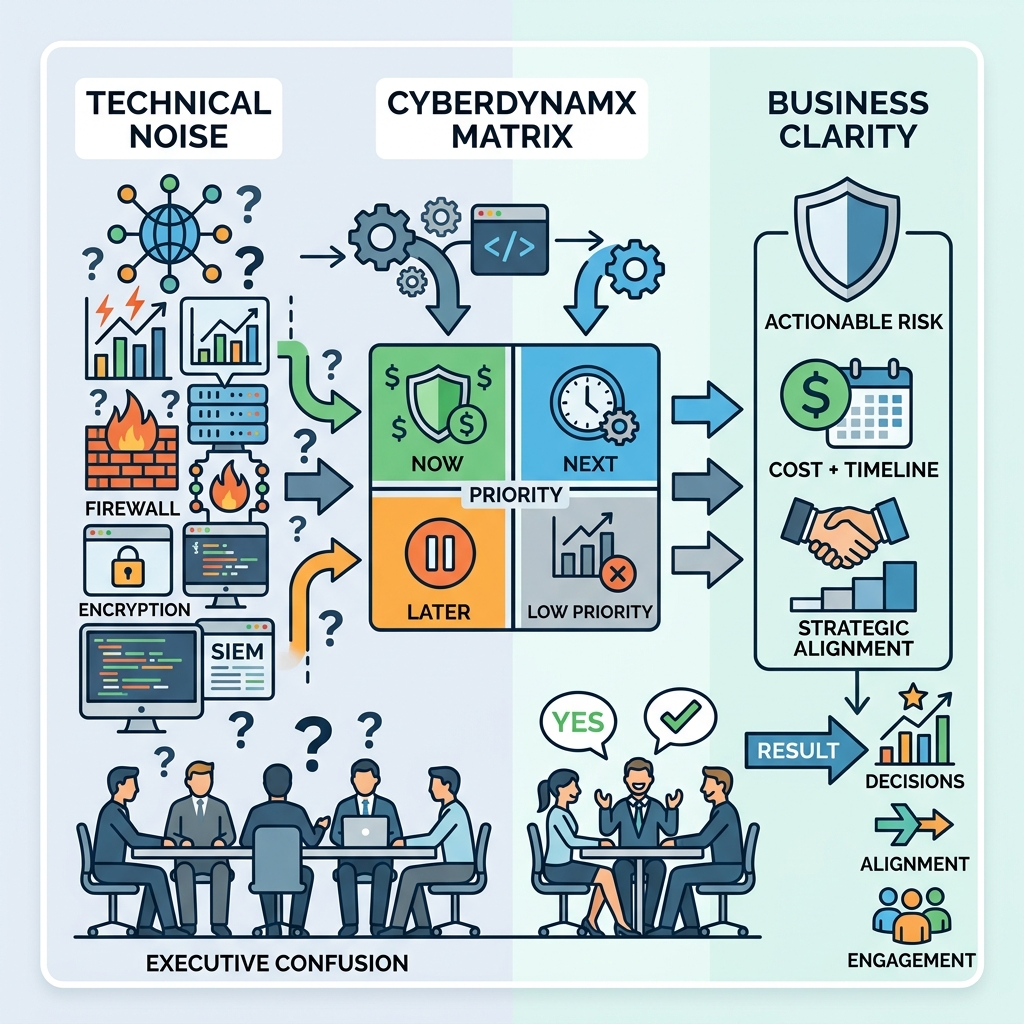
Cybersecurity leaders often know exactly what the risks are — but struggle to communicate them in a way executives can act on. Technical jargon, tool‑centric explanations, and overly detailed descriptions create confusion instead of clarity.
The truth is simple: Cyber risk must be communicated in business language.
Executives don’t need to understand encryption algorithms, firewall rules, or SIEM correlation logic. They need to understand impact, likelihood, priority, and business consequences.
This is where many cybersecurity programs break down.
Why Technical Communication Fails
Technical explanations often:
- Overwhelm leadership
- Hide the real risk behind details
- Make cybersecurity seem more complex than it is
- Create disconnect between IT and executives
- Slow down decision‑making
- Reduce confidence in cybersecurity leadership
Executives don’t need more data — they need a clear story.
What Leaders Actually Want to Know
When communicating cyber risk, executives want answers to five questions:
- What is the risk? (Plain language, no jargon.)
- Why does it matter? (Business impact.)
- How likely is it? (Maturity + exposure.)
- What should we do first? (Prioritization.)
- What will it cost? (Resources + timeline.)
If you answer these clearly, leadership will engage.
How the CyberDynamX Matrix Helps
The Matrix is one of the most powerful communication tools available because it:
- Shows all cyber risks on one page
- Highlights the highest‑risk gaps
- Groups them into NOW / NEXT / LATER
- Removes technical complexity
- Creates a shared language for decision‑making
- Helps executives understand maturity at a glance
Instead of explaining 106 subcategories, you show the Matrix — and the conversation becomes instantly clearer.
Governance Also Supports Communication
The CyberDynamX Governance Enablement Program strengthens communication by providing:
- Clear policies
- Defined roles
- Consistent standards
- Executive‑ready governance materials
- Board‑level security overview decks (Tier 3)
These artifacts help leadership understand expectations and responsibilities.
The Result
Organizations gain:
- Faster decisions
- Better alignment
- Stronger leadership engagement
- Clearer prioritization
- Higher maturity
Cyber risk becomes understandable — and actionable.
Get The Assessment: The Assessment
