
One of the most common weaknesses in cybersecurity assessments is not the framework being used. It is the assumption that one person can accurately answer every question.
Modern cybersecurity programs span identity and access management, cloud platforms, incident response, vendor risk management, governance, disaster recovery, compliance, and countless other disciplines. Even the most experienced cybersecurity professional cannot possess deep operational knowledge of every area across the organization.
Yet many cybersecurity assessments are still completed by a single individual.
The result is often an incomplete picture of organizational maturity, where some capabilities are overestimated, others are underestimated, and critical gaps remain hidden behind assumptions.
Organizations achieve better outcomes when assessments capture the knowledge of the people closest to the work.
Why Delegation Matters
Cybersecurity has become a multidisciplinary business function. Responsibilities are distributed across technical teams, operational departments, leadership groups, vendors, and third-party service providers.
An Identity and Access Management specialist understands access controls differently than a cloud architect. A procurement team often has greater visibility into vendor risk practices than a cybersecurity analyst. Executive leaders typically understand governance, accountability, and strategic decision-making in ways that operational teams do not.
Expecting a single individual to accurately represent all of these perspectives creates an unnecessary risk within the assessment process itself.
The most reliable assessments are built from collective expertise rather than individual opinion.
When organizations engage subject matter experts across multiple domains, the resulting assessment becomes a far more accurate reflection of reality.
The Challenge With Single-Responder Assessments
Single-responder assessments often create unintended blind spots.
Without direct expertise in every functional area, respondents may answer questions based on assumptions, limited visibility, or best estimates. In many cases, answers reflect how a process is expected to work rather than how it actually operates in practice.
This can lead to inflated maturity scores, overlooked weaknesses, misunderstood controls, and gaps that remain undiscovered until an audit, security review, or incident reveals them.
Perhaps most concerning, leadership receives information that appears authoritative but may not fully represent organizational reality. Decisions, investments, and priorities are then based on an incomplete understanding of the organization’s actual cybersecurity capabilities.
The issue is rarely competence. It is simply the reality that no single person sees everything.
How Unlimited Delegations Improve Assessment Quality
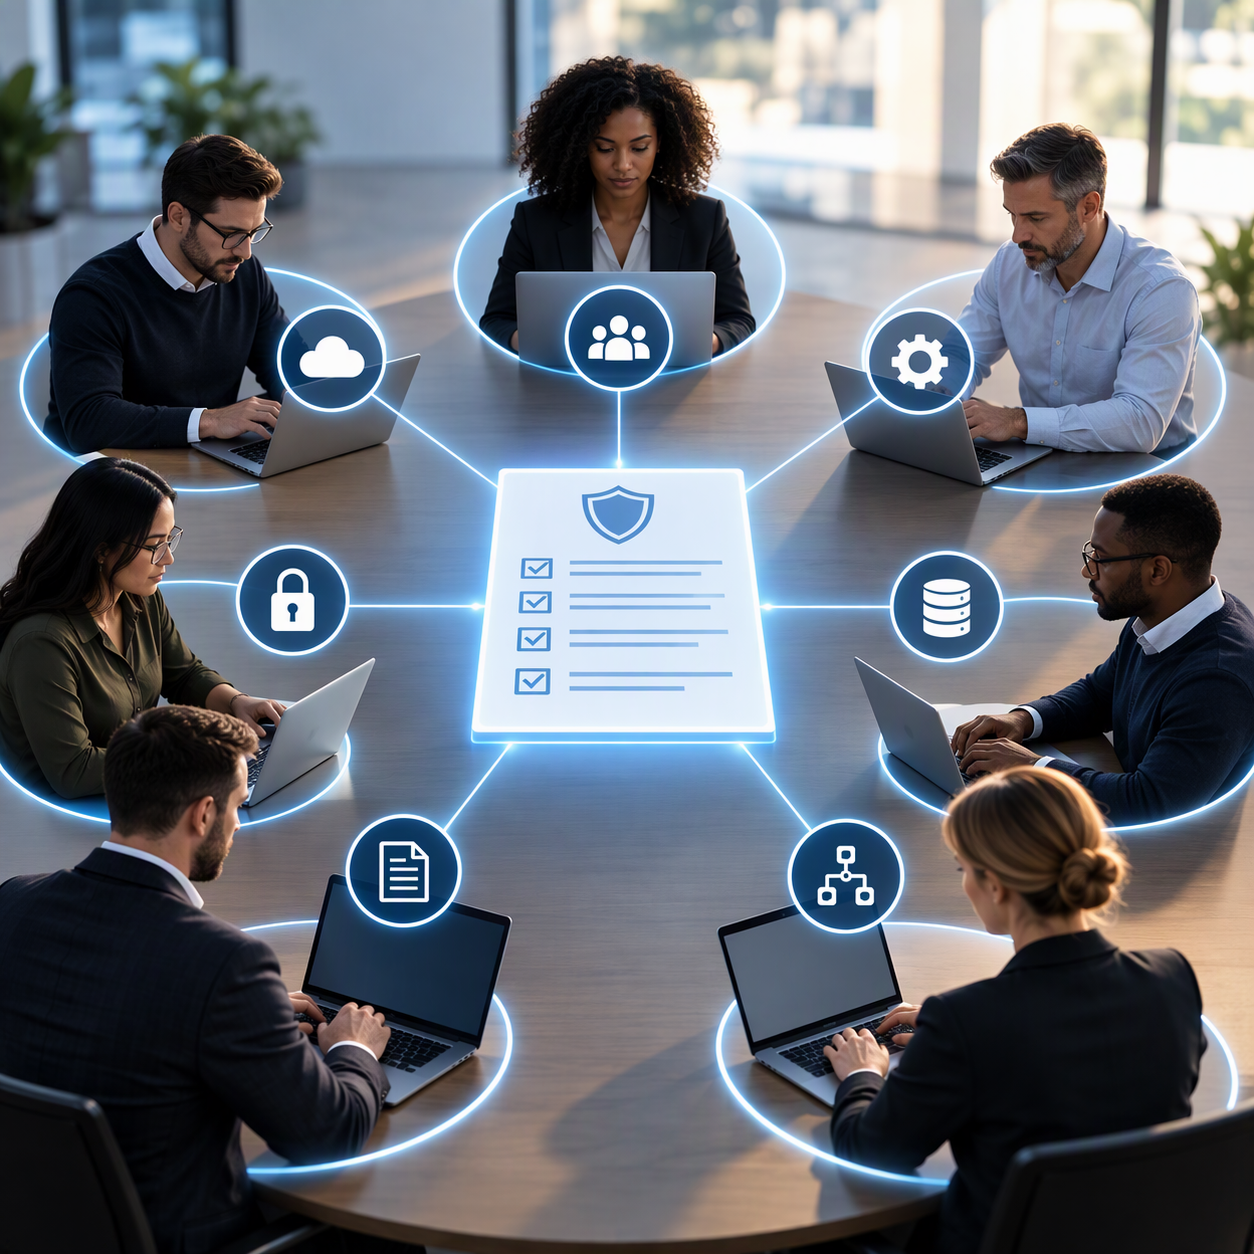
The CyberDynamX Assessment Program addresses this challenge through Unlimited Delegations, allowing organizations to distribute assessment questions to the individuals best positioned to answer them.
Questions related to identity management can be assigned to IAM specialists. Cloud security topics can be reviewed by cloud engineers. Vendor management controls can be validated by procurement teams. Governance and oversight questions can be directed to leadership. Incident response capabilities can be assessed by security operations personnel, while recovery and continuity questions can be reviewed by IT operations teams.
This approach transforms the assessment process from a single viewpoint into a collaborative organizational exercise.
More importantly, it creates a richer evidence base. Responses are provided by those who directly manage the relevant processes, controls, and technologies on a daily basis. The result is greater accuracy, reduced bias, and stronger confidence in the final assessment outcomes.
Why Accuracy Matters
An assessment is only valuable if decision-makers trust the results.
When maturity scores accurately reflect operational reality, organizations can prioritize improvement initiatives with greater confidence. Resources can be directed toward the areas of greatest need, recommendations become more effective, and leadership gains a clearer understanding of where investments will have the greatest impact.
Accurate assessments also improve conversations between technical teams and executives. Rather than debating the validity of the results, organizations can focus on what matters most: reducing risk, improving capabilities, and driving measurable progress.
In this way, assessment accuracy becomes the foundation for meaningful maturity improvement.
The Result
Organizations that leverage a broader range of expertise during the assessment process gain a more complete understanding of their cybersecurity environment. They reduce bias, improve alignment across teams, strengthen decision-making, and create a more reliable picture of organizational maturity.
The goal of a cyber maturity assessment should not be to confirm assumptions. It should be to uncover reality.
By ensuring the right questions are answered by the right people, organizations move closer to that reality and position themselves to make better cybersecurity decisions moving forward.
Ultimately, the most accurate assessment is rarely the one completed by a single expert. It is the one informed by the collective expertise of the entire organization.
Get The Assessment
