-
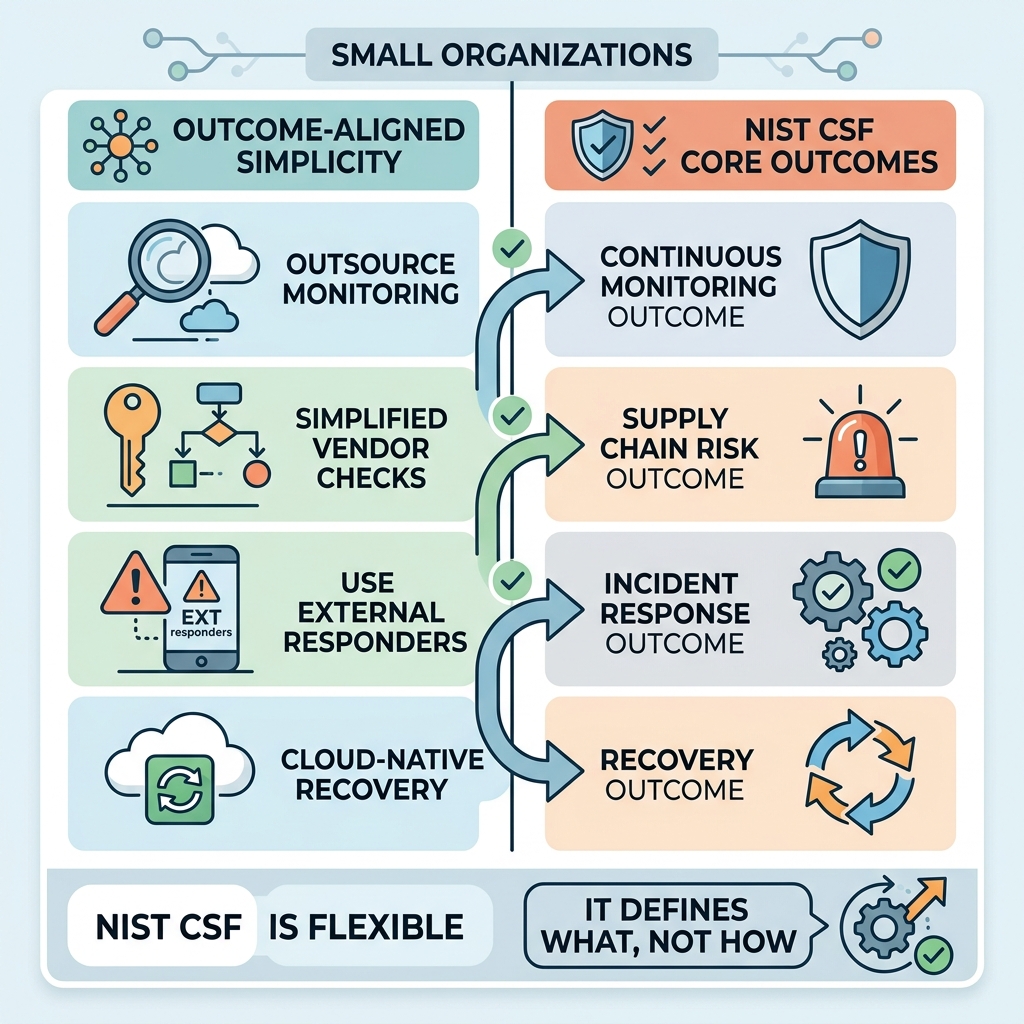
Every NIST CSF Outcome Applies — Even If You Implement It Differently
Read more: Every NIST CSF Outcome Applies — Even If You Implement It DifferentlySmall organizations often say, “That part of NIST CSF doesn’t apply to us.” But when you examine the outcomes, every one of them applies — even if the implementation looks different. For example: The outcome is the same. The method is different. NIST CSF is flexible by design. It defines what must be true…
-
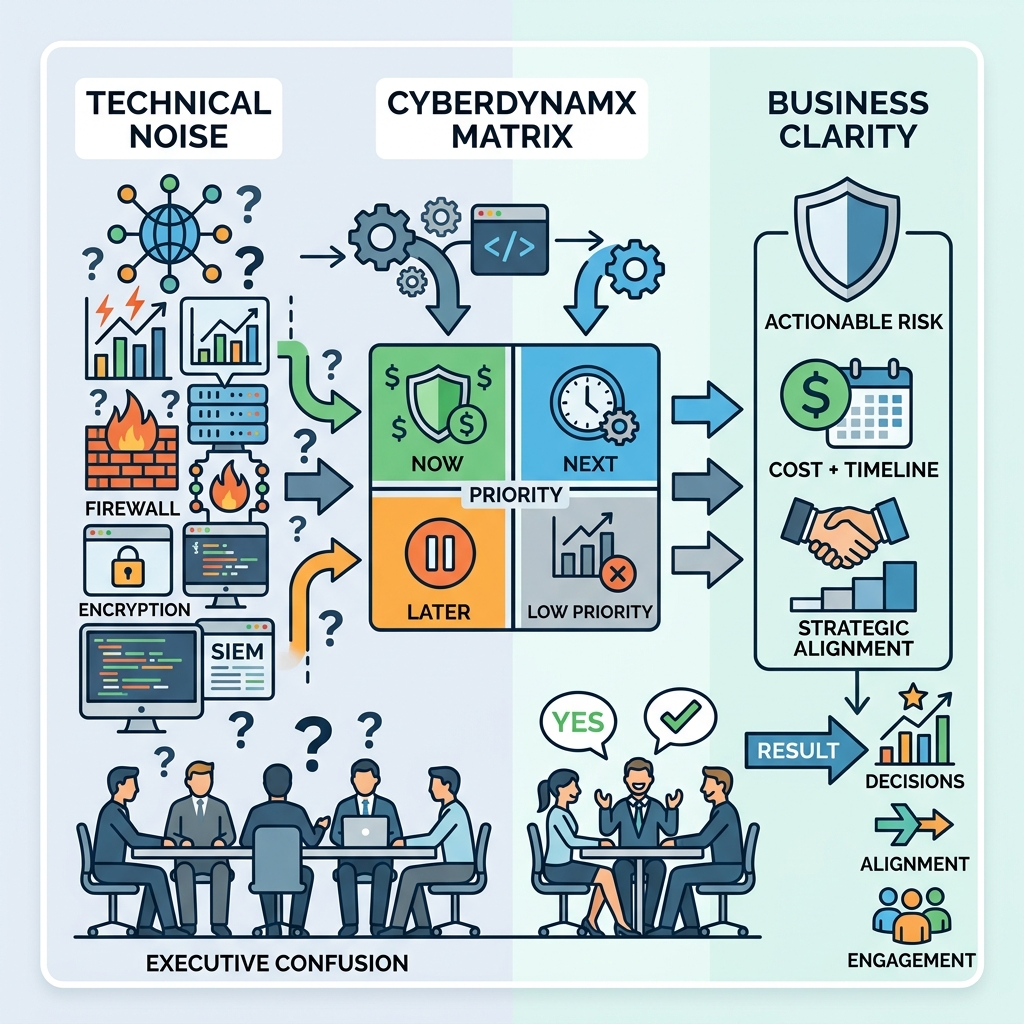
How to Communicate Cyber Risk Without Technical Jargon
Read more: How to Communicate Cyber Risk Without Technical JargonCybersecurity leaders often know exactly what the risks are — but struggle to communicate them in a way executives can act on. Technical jargon, tool‑centric explanations, and overly detailed descriptions create confusion instead of clarity. The truth is simple: Cyber risk must be communicated in business language. Executives don’t need to understand encryption algorithms,…
-
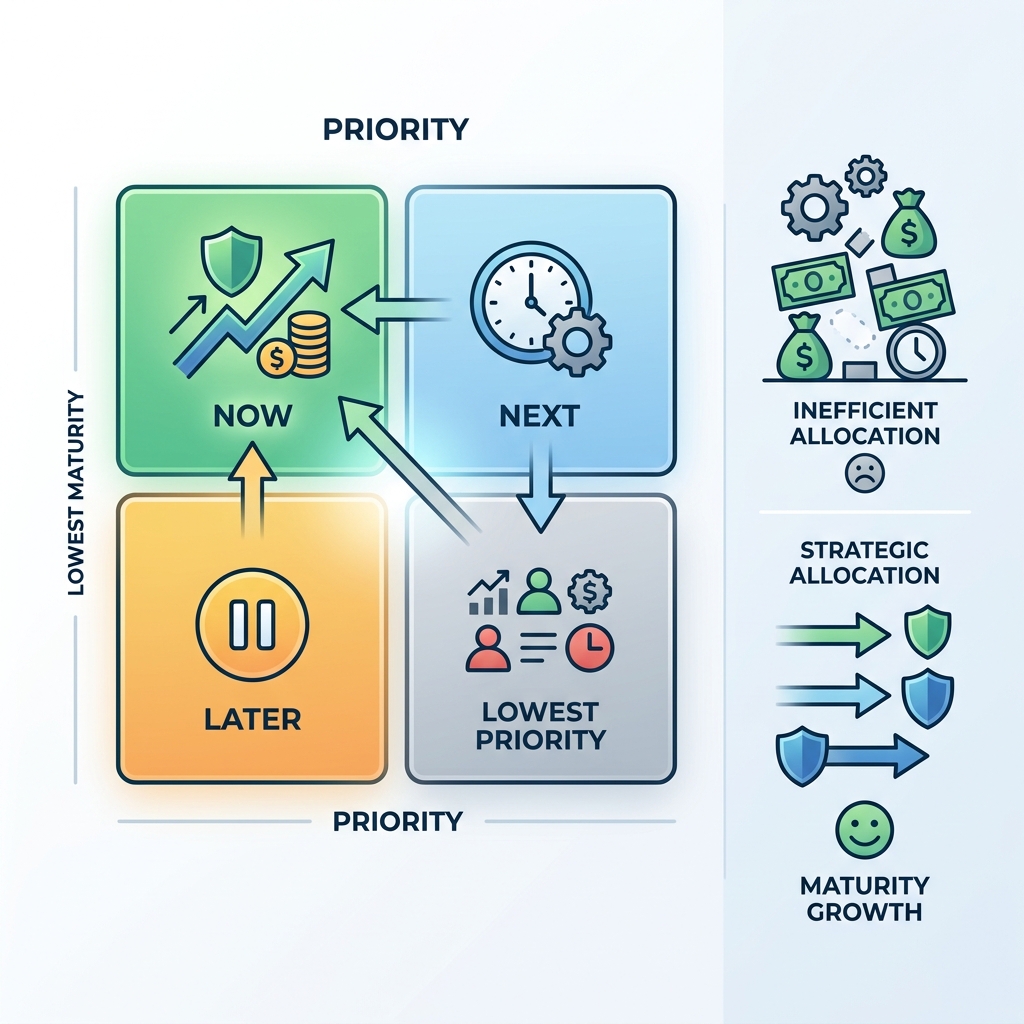
The Cost of Fixing the Wrong Cyber Problems First
Read more: The Cost of Fixing the Wrong Cyber Problems FirstCybersecurity resources are limited. Time, budget, staffing, and attention must be allocated carefully. When organizations fix the wrong problems first, they waste resources and leave high‑risk gaps unaddressed. This is one of the most common — and most costly — cybersecurity mistakes. Why Organizations Fix the Wrong Problems Organizations often misprioritize because: The result…
-
Evidence‑Based Validation: The Cure for Over‑Optimistic Cyber Assessments
Read more: Evidence‑Based Validation: The Cure for Over‑Optimistic Cyber AssessmentsSelf‑assessments are valuable — but they’re also vulnerable to bias. Many organizations unintentionally over‑estimate their maturity, believing processes are stronger or more consistent than they actually are. This creates false confidence and hidden risk. Evidence‑based validation solves this problem. The CyberDynamX Assessment Program includes randomized evidence reviews for items scoring 3.00 or higher. This…
-
Cyber Maturity as a Business Strategy, Not a Compliance Exercise
Read more: Cyber Maturity as a Business Strategy, Not a Compliance ExerciseCyber maturity is often misunderstood as a compliance requirement. Organizations treat it as a checkbox activity — something they must do to satisfy auditors or regulators. But cyber maturity is not compliance. It’s strategy. A mature cybersecurity program reduces risk, strengthens resilience, improves operational stability, and builds customer trust. It’s a competitive advantage —…
-
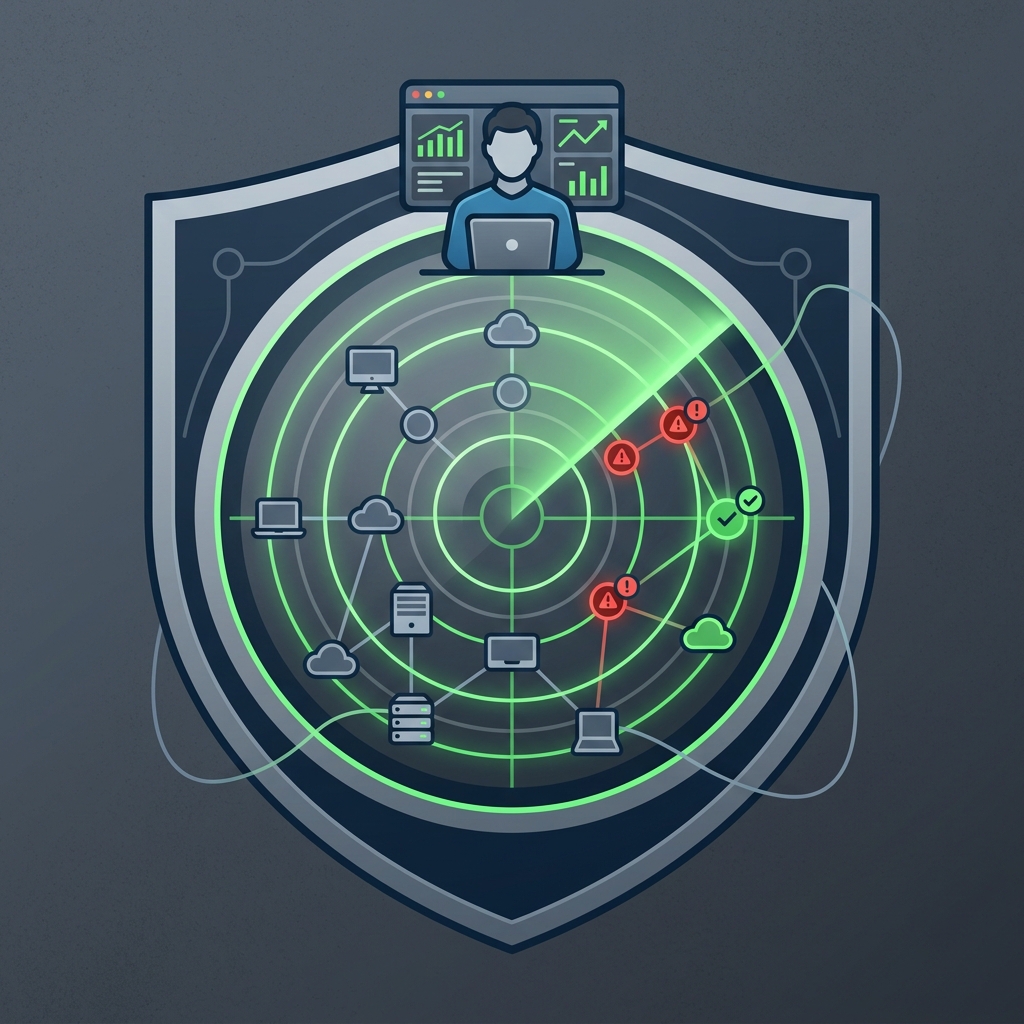
Why Continuous Monitoring Scores Lag in Most Organizations
Read more: Why Continuous Monitoring Scores Lag in Most OrganizationsContinuous monitoring is one of the most important cybersecurity capabilities — and one of the most commonly underdeveloped. Many organizations score low in this category, often falling into the NOW priority tier. This isn’t due to lack of effort. It’s due to the complexity of monitoring modern environments. Why Continuous Monitoring Is Challenging Organizations…
-
How Tailored Governance Materials Accelerate Organizational Adoption
Read more: How Tailored Governance Materials Accelerate Organizational AdoptionCybersecurity governance often fails not because the documents are wrong — but because they don’t feel like they belong to the organization. Policies, standards, and procedures copied from templates or borrowed from other companies rarely fit the environment they’re meant to protect. That’s why tailored governance materials matter. The CyberDynamX Governance Enablement Program customizes…
-
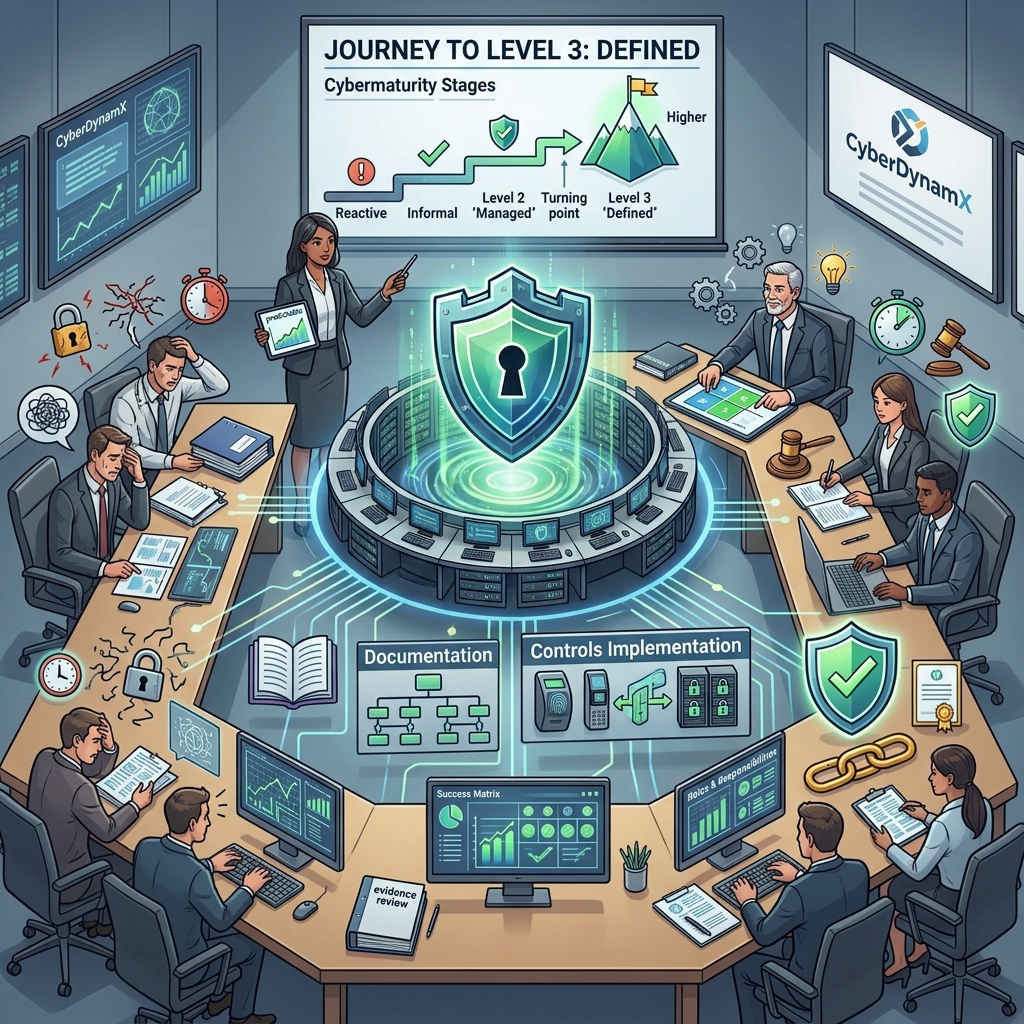
Why Level 3 (“Defined”) Is the Turning Point for Most Organizations
Read more: Why Level 3 (“Defined”) Is the Turning Point for Most OrganizationsCyber maturity grows in stages. Organizations move from reactive behavior to proactive behavior, from informal processes to defined processes, and from inconsistent implementation to consistent execution. The turning point in this journey is Level 3: Defined. This is the maturity level where cybersecurity becomes stable, predictable, and repeatable. It’s the point where risk begins…
-
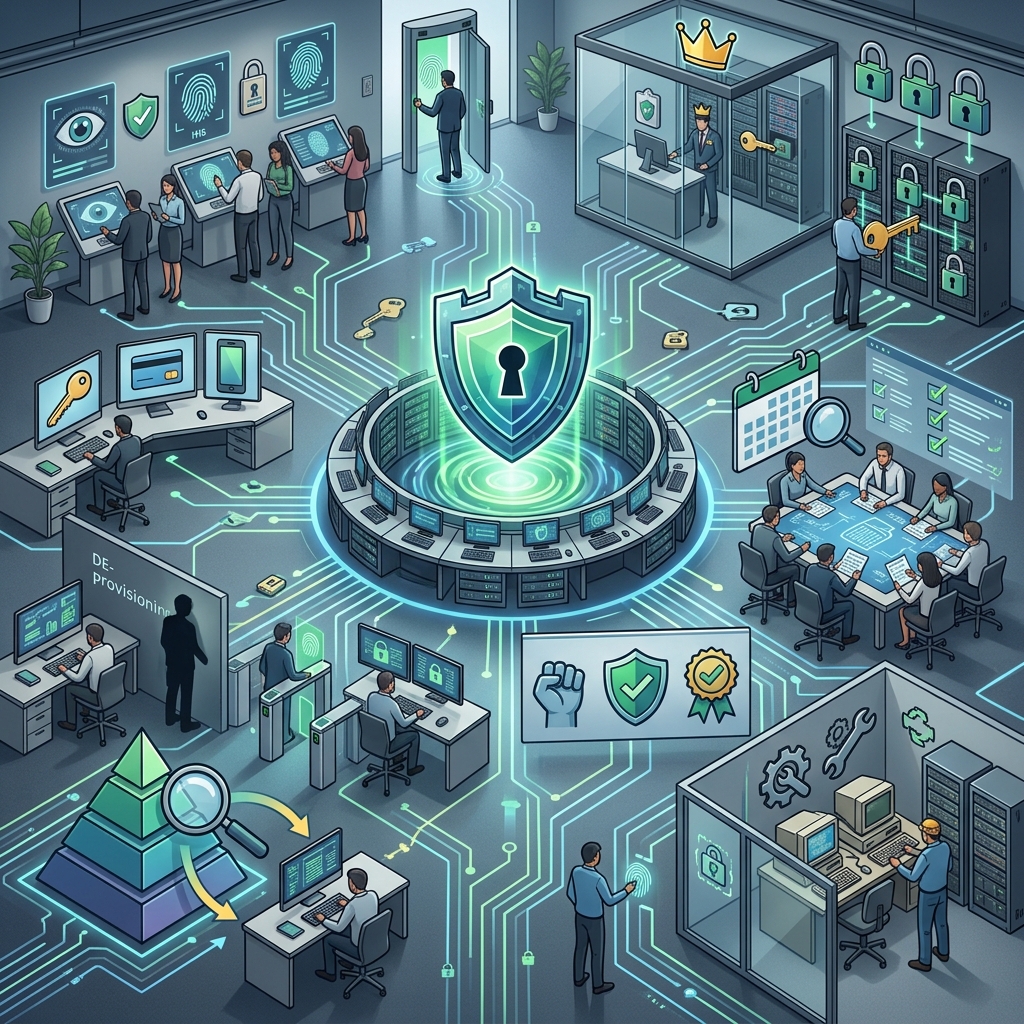
Identity & Access Management: Why It’s Often the Weakest Link
Read more: Identity & Access Management: Why It’s Often the Weakest LinkIdentity and Access Management (IAM) is one of the most critical components of cybersecurity — and one of the most commonly underdeveloped. In many assessments, IAM categories score significantly lower than others, often falling into the NOW priority tier. This isn’t surprising. IAM touches every system, every user, and every workflow. When it’s weak,…
-
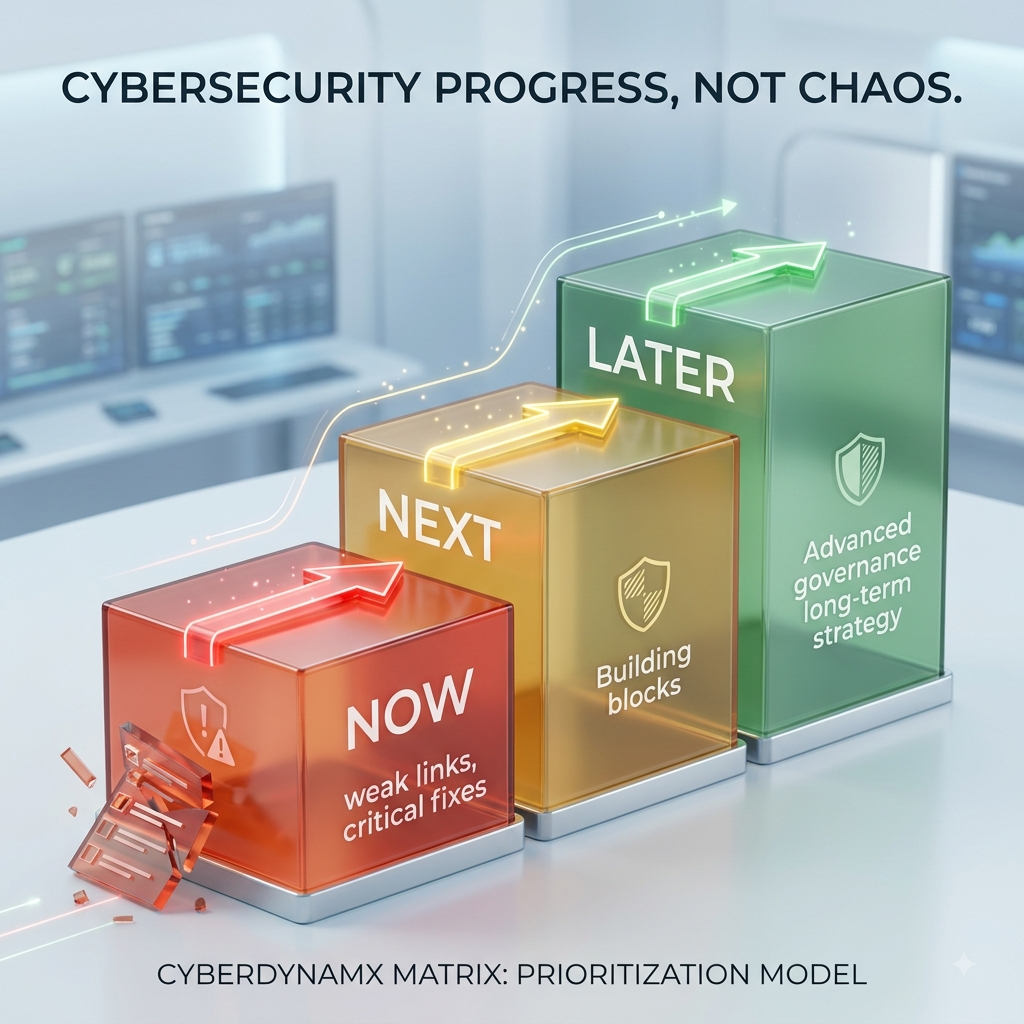
NOW / NEXT / LATER: A Smarter Way to Prioritize Cyber Improvements
Read more: NOW / NEXT / LATER: A Smarter Way to Prioritize Cyber ImprovementsCybersecurity improvement often fails because organizations try to fix everything at once. They create long lists of recommendations, assign dozens of tasks, and attempt to tackle every gap simultaneously. The result is predictable: stalled progress, overwhelmed teams, and misaligned priorities. The CyberDynamX Matrix solves this problem with a simple but powerful model: NOW /…

News & Updates
Buy my book
The Art and Science of Building a Simplified Digital Security Program
In CyberDynamX, I guide you through the process of creating a structured, resilient digital security program tailored to meet your organization’s unique needs. This approach helps integrate security seamlessly into daily operations, setting the foundation for a proactive cybersecurity culture.
- Master risk management and build a risk-aware culture.
- Classify and secure essential data assets.
- Design a governance framework with robust security architecture.
- Establish clear policies, standards, and control measures.
- Implement resilient strategies without relying on “quick fixes.”

I’ve had the privilege of working with Curtis on some really cool things this past year. He’s a trusted source, whip smart, super humble, and an all-around great guy. If you’re employed in any cyber security role regardless if you’re just starting out or have a few battle scars, his book is probably something you want to add to your library.
Director, Cybersecurity & CISO
MacEwan University
Curtis has proven to be a strong and highly knowledgeable professional who has served our organization very well…
CIO
Alberta Blue Cross
I believe the book is well positioned to be a thought-leader and practical guide for organizations looking to establish a solid security posture. I love how the book transcends the commercial and not-for-profit sectors, and is applicable to companies in Canada, the US, and internationally. Highly recommended and worth every penny!
CISO
MRNET
…you speak with humility, something that makes you very approachable, especially to people who may not have the confidence of those more established in the field. Cybersecurity needs more people like you.
Chief Information Security Officer
University of Northern BC
Curtis’ leadership and guidance in advancing cybersecurity programs within Canada’s higher education sector highlight his deep expertise in risk management and his commitment to high standards.
Chief Information Security Officer
British Columbia Institute of Technology
Much of your work regarding IT Security Governance has remained as the foundation for effective operations. And it provided an excellent foundation that we could expand upon. Your great work, and its cumulative impacts, set us up for future success in a lot of regards. Also, our Enterprise Architect is a big fan.
Director of Information, Risk & Compliance
NorQuest College
I have been consistently impressed by Curtis' professional competency and solid knowledge in the IT security, compliance and governance disciplines.
Sr. Manager
Alberta Blue Cross
I wish that I’d had this book when I was starting out in cyber security. It would have saved me from making many common and uncommon mistakes, leaving me free to find new and creative mistakes of my own to make.
Chief Information Security Officer
University of Northern BC
Curtis is one of the most creative mind I know, and taught me to think outside of the box…
Senior Security Consultant
TELUS
Curtis is a strategic 21st Century thinker and doer and he has a vision that captures the imagination. Curtis is a highly regarded leader in the security community.
CSO / Canadian Security Director of the Year
TELUS
Curtis is a pragmatic strategist who emphasizes risk reduction and digital resilience by implementing effective controls in key areas to thwart one's adversaries.
Field CTO Cybersecurity
Cisco Canada
He always demonstrates professionalism in every facet of business and has a proven record of success as a leader…
Director, National Solutions Delivery
TELUS
I still have the materials and lessons learned from the leadership program you did for us!
Manager Server Infrastructure & Operations
Alberta Blue Cross
Curtis is a leader, humble, creative, and has a tremendous amount of integrity.
Team Manager
Alberta Blue Cross
He is a visionary…
CTO
ATB Financial
If you’re looking for someone with that rare combination of character, vision and leadership, who can still roll up their sleeves to get things done, meet Curtis Blais.
President
SC Canada Services Inc.
Curtis is the definition of professionalism. He is one of the most knowledgeable professionals it is my pleasure to know in the areas of Security and Compliance.
Your work has been sooo helpful!
Director, Information Technology
Olds College
I'm a practical person, and I don't like to fall into excessive praising, but I chose my words lightly when I say you were very inspiring.
Sr. Consultant/Manager
KPMG
I've never worked with a person with more integrity.
Information Security Analyst
AIMCo