-
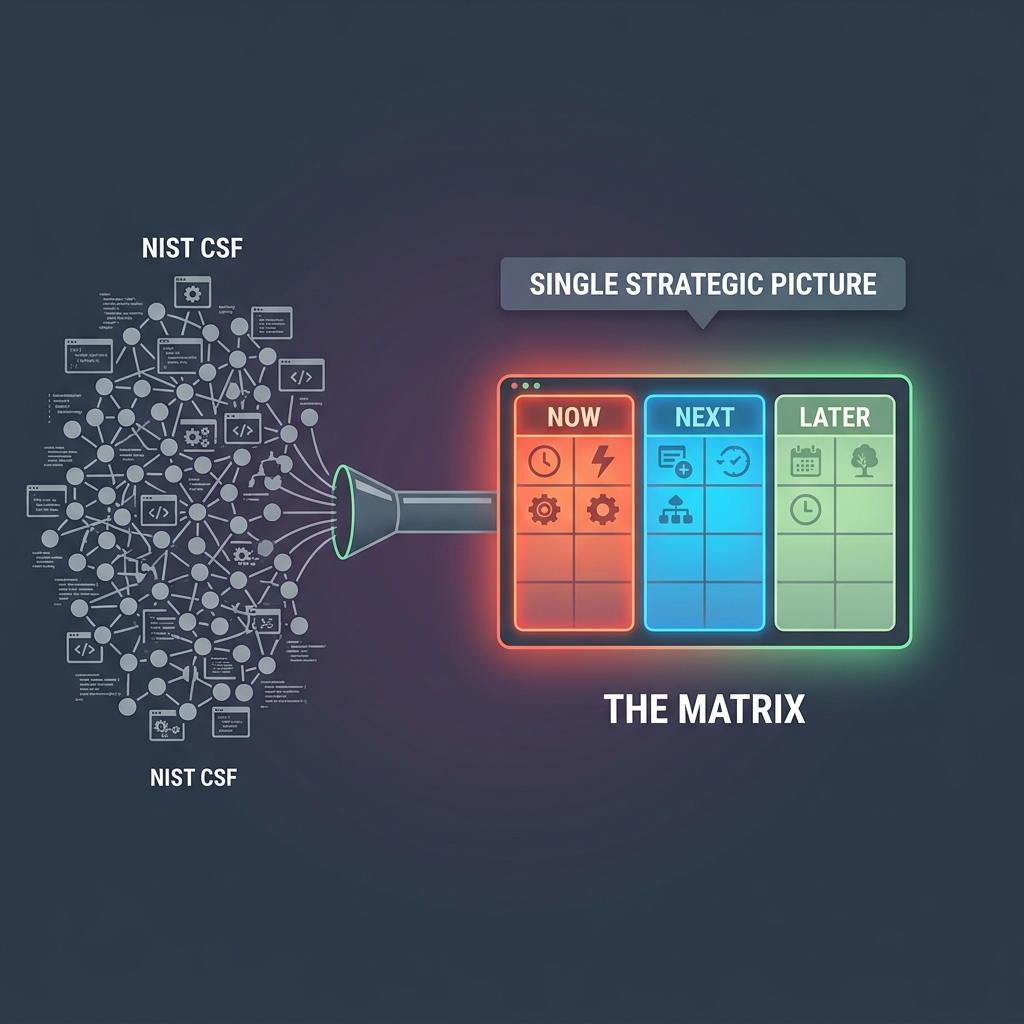
How the Matrix Turns 106 Subcategories Into a Single Strategic Picture
Read more: How the Matrix Turns 106 Subcategories Into a Single Strategic PictureCybersecurity frameworks are powerful, but they’re also overwhelming. NIST CSF 2.0 contains 106 subcategories, each representing a specific cybersecurity outcome. For most organizations, understanding all 106 — let alone prioritizing them — is nearly impossible. That’s why the CyberDynamX Matrix is such a breakthrough. The Matrix takes all 106 subcategories and transforms them into…
-
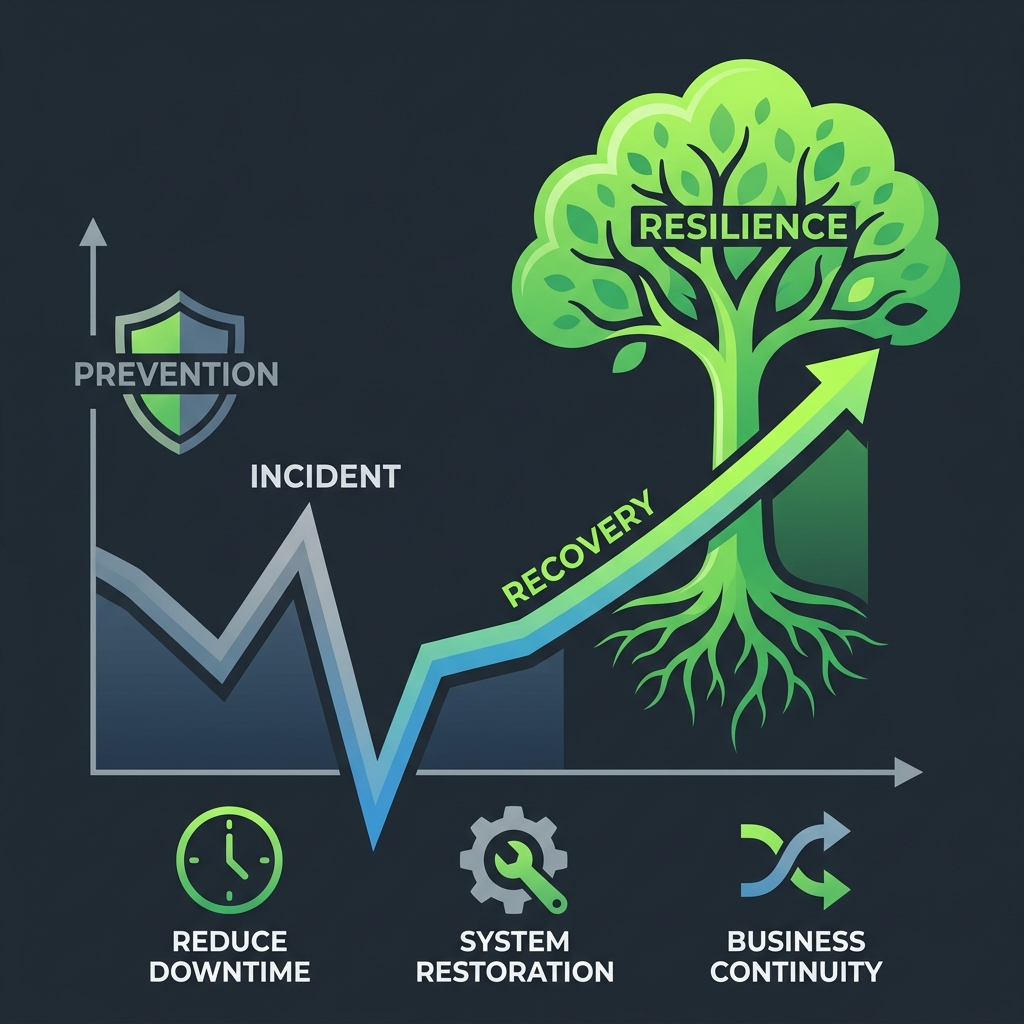
Why Recovery Planning Matters More Than Prevention
Read more: Why Recovery Planning Matters More Than PreventionPrevention is important — but recovery determines resilience. No matter how strong your cybersecurity program is, incidents will still occur. What matters most is how quickly and effectively you can recover. Recovery planning is one of the most critical — and most overlooked — cybersecurity capabilities. Why Recovery Scores Are Often Low Organizations struggle…
-
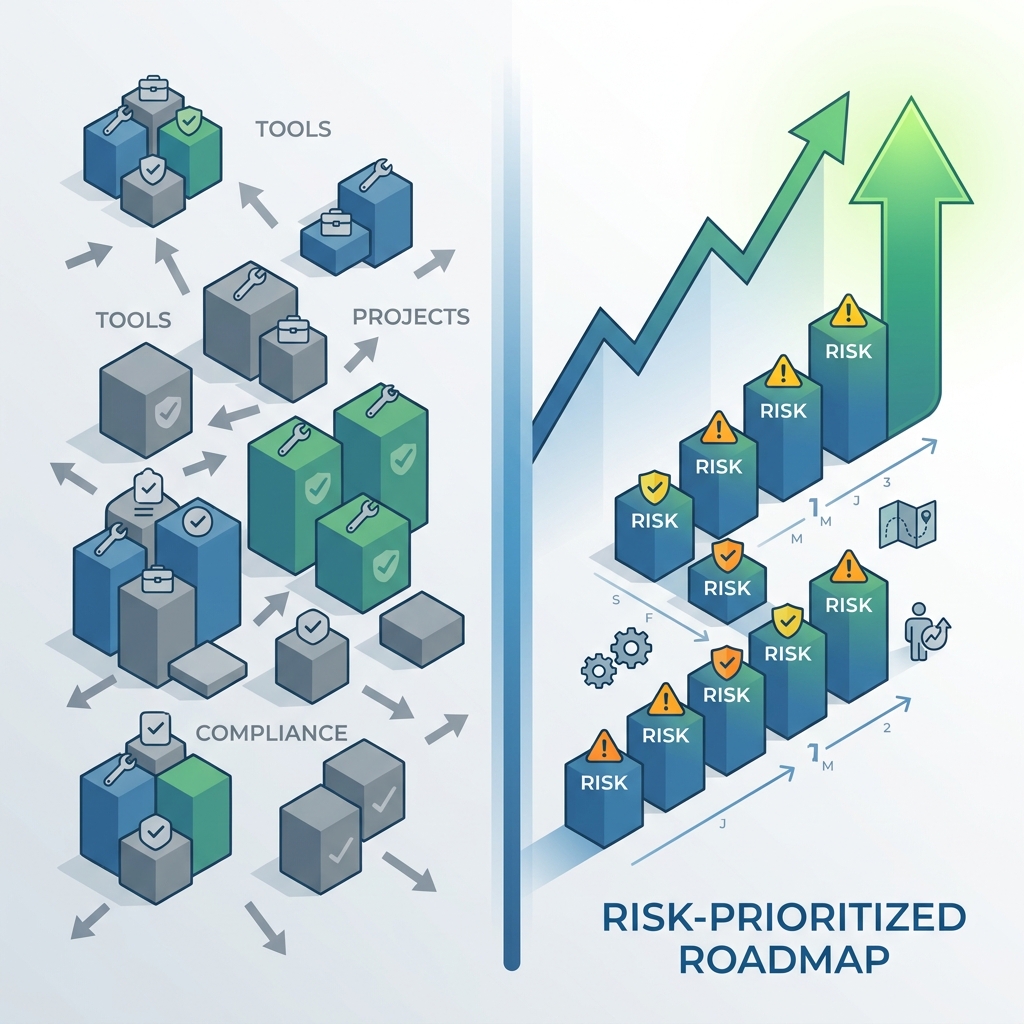
How Risk‑Prioritized Roadmaps Accelerate Cyber Maturity
Read more: How Risk‑Prioritized Roadmaps Accelerate Cyber MaturityCybersecurity roadmaps are often created based on tools, projects, or compliance requirements — not risk. This leads to misaligned priorities, wasted resources, and slow maturity growth. Risk‑prioritized roadmaps solve this problem. They align cybersecurity improvements with the organization’s highest‑risk gaps, ensuring resources are used where they matter most. Why Roadmaps Matter Roadmaps: But only…
-
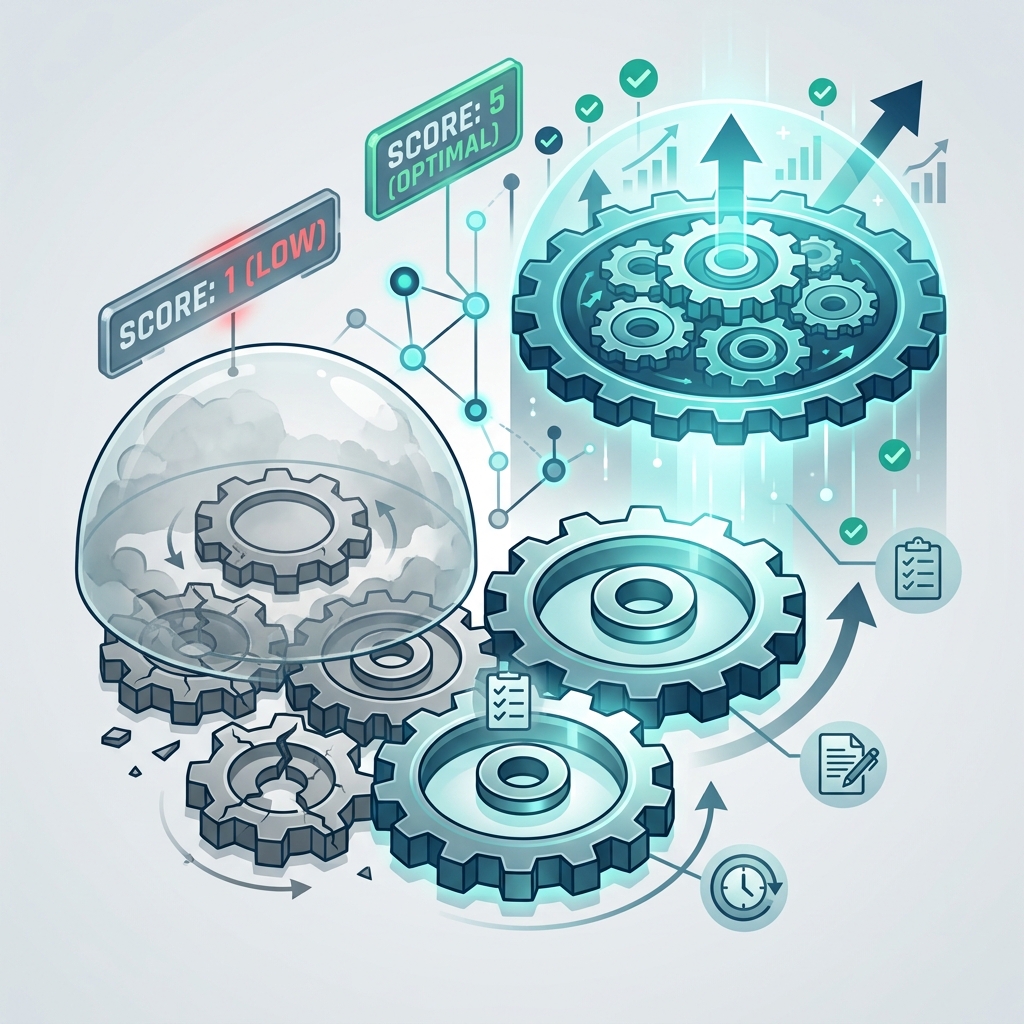
Why Improvement (ID.IM) Is the Most Undervalued NIST Category
Read more: Why Improvement (ID.IM) Is the Most Undervalued NIST CategoryThe Improvement category (ID.IM) is one of the most undervalued — and most important — parts of the NIST Cybersecurity Framework. It focuses on continuous evaluation and improvement, ensuring cybersecurity practices evolve with the organization and the threat landscape. Yet many organizations score extremely low in this category. Why Improvement Scores Are Low Organizations…
-
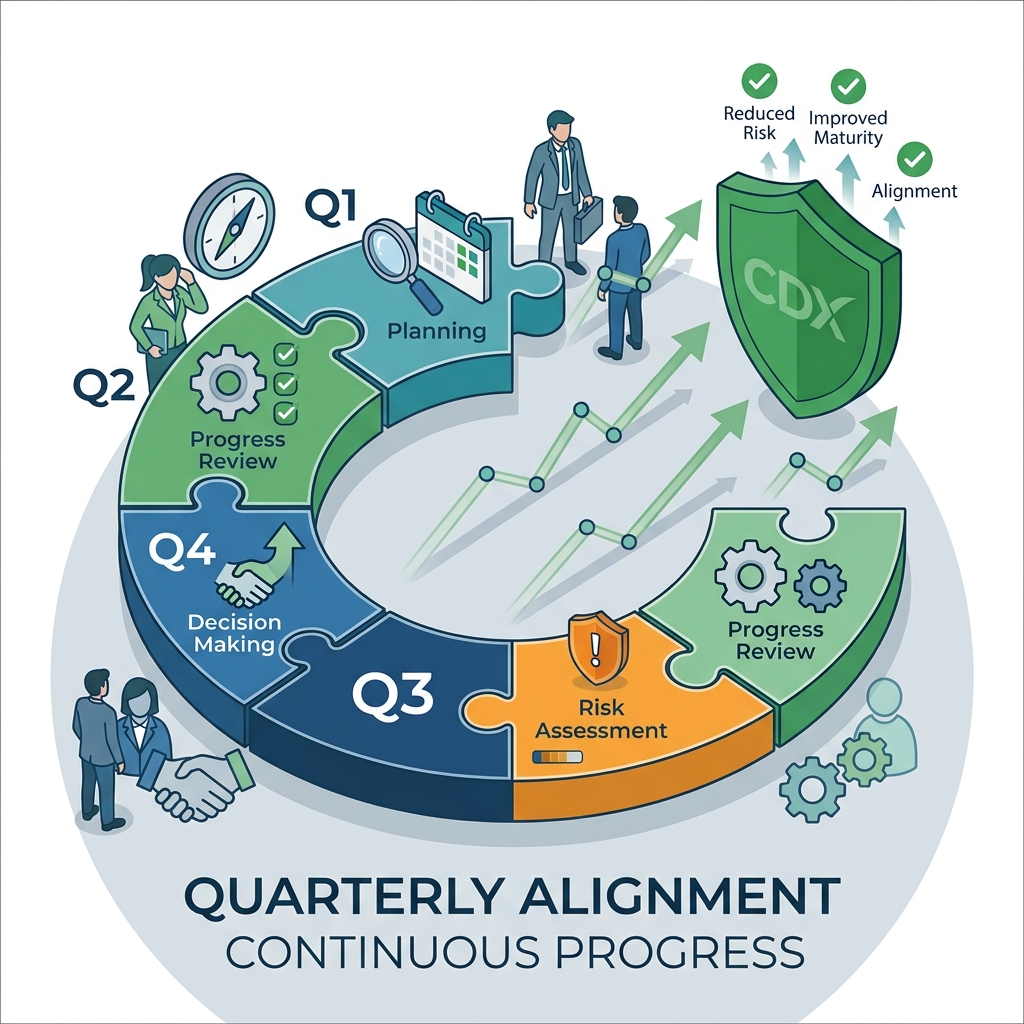
How Quarterly Cyber Check‑Ins Keep Organizations Aligned
Read more: How Quarterly Cyber Check‑Ins Keep Organizations AlignedCybersecurity is not a one‑time project — it’s an ongoing discipline. Organizations that treat cybersecurity as an annual activity often fall behind, lose momentum, and struggle to maintain alignment. Quarterly cyber check‑ins solve this problem. These short, structured sessions keep leadership, IT, and security aligned on priorities, progress, and emerging risks. Why Quarterly Check‑Ins…
-
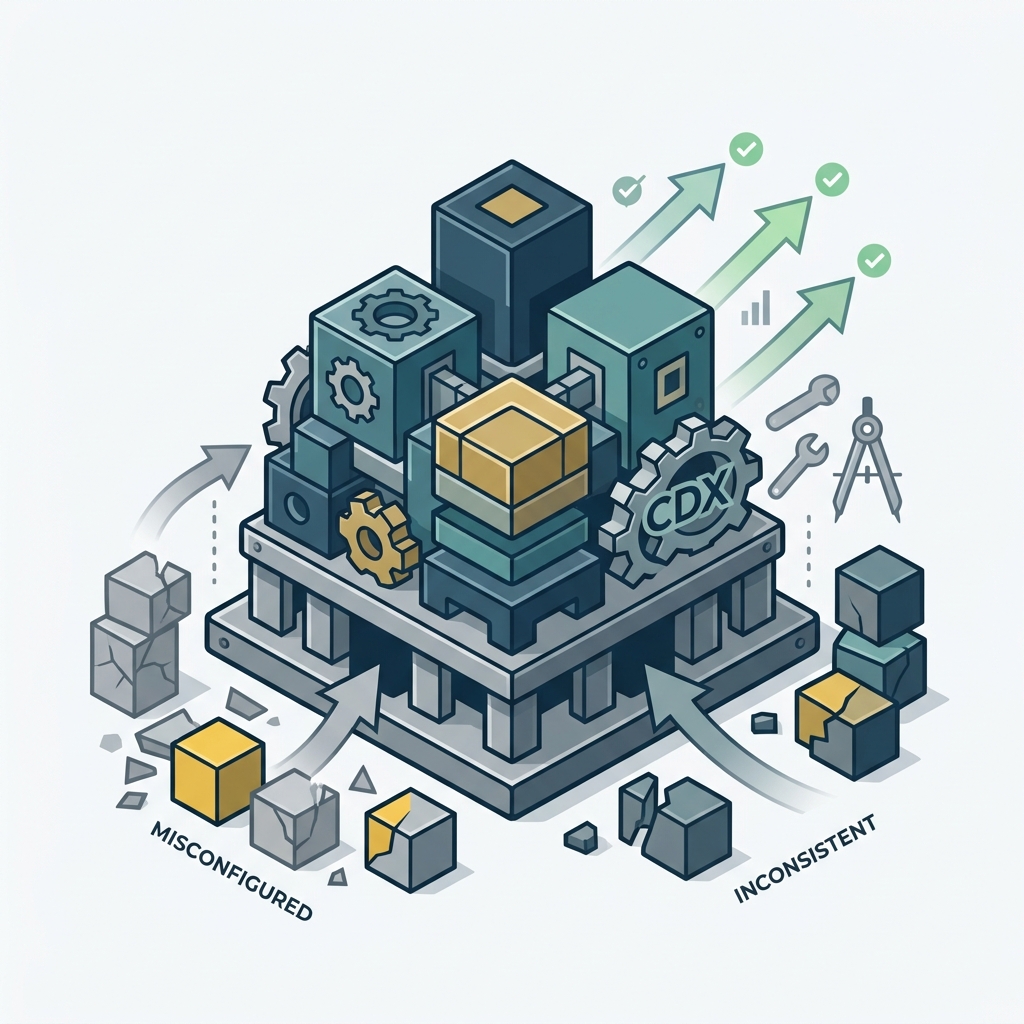
The Hidden Risks in Platform Security and Configuration Management
Read more: The Hidden Risks in Platform Security and Configuration ManagementPlatform security and configuration management are foundational cybersecurity capabilities — yet they are often underdeveloped. Many organizations score lower in this category than expected, revealing hidden risks that can lead to major incidents. Configuration management determines how secure your systems truly are. Why Platform Security Scores Are Low Organizations struggle with platform security because:…
-
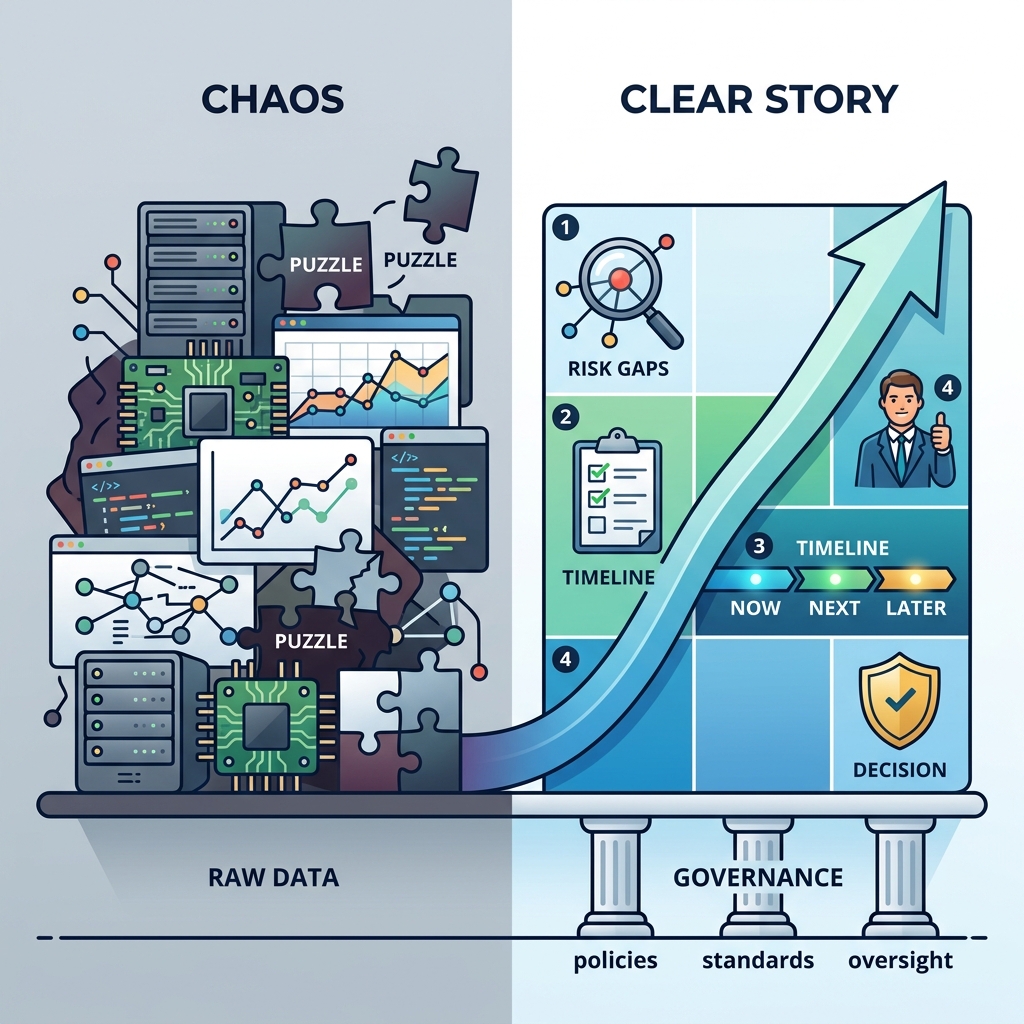
Why Boards Need a Clear Cyber Story, Not More Data
Read more: Why Boards Need a Clear Cyber Story, Not More DataBoards are increasingly responsible for overseeing cybersecurity risk — but they are not cybersecurity experts. They don’t need technical details, dashboards, or tool‑specific metrics. They need a clear, concise, and defensible cyber story. A cyber story explains: This is far more valuable than raw data. Why Boards Struggle With Cybersecurity Boards often feel overwhelmed…
-
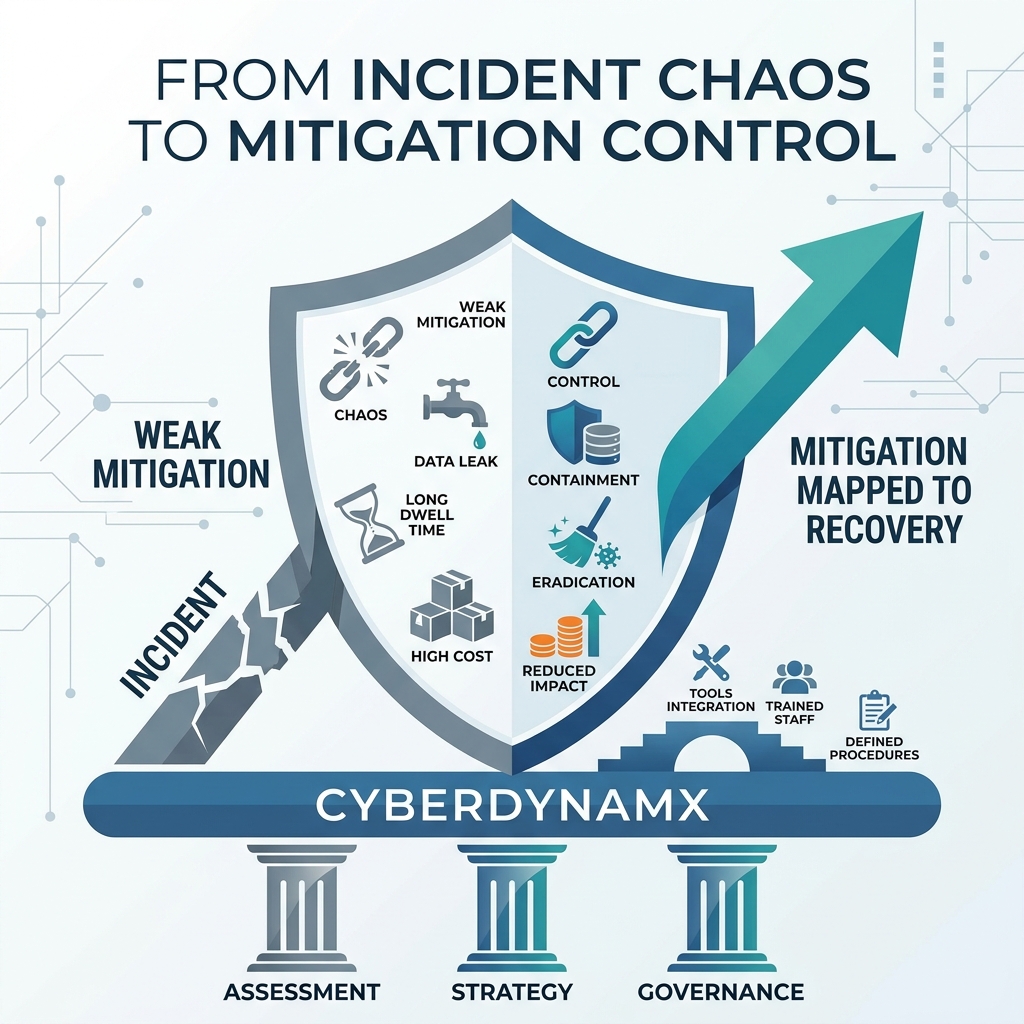
Incident Mitigation: The Category Where Organizations Score 1.00
Read more: Incident Mitigation: The Category Where Organizations Score 1.00Incident mitigation is one of the most critical cybersecurity capabilities — and one of the most commonly underdeveloped. In many assessments, organizations score 1.00 in this category, indicating reactive, incomplete, or nonexistent processes. This is dangerous. Incident mitigation determines whether an incident becomes a minor disruption or a major breach. Why Incident Mitigation Scores…
-
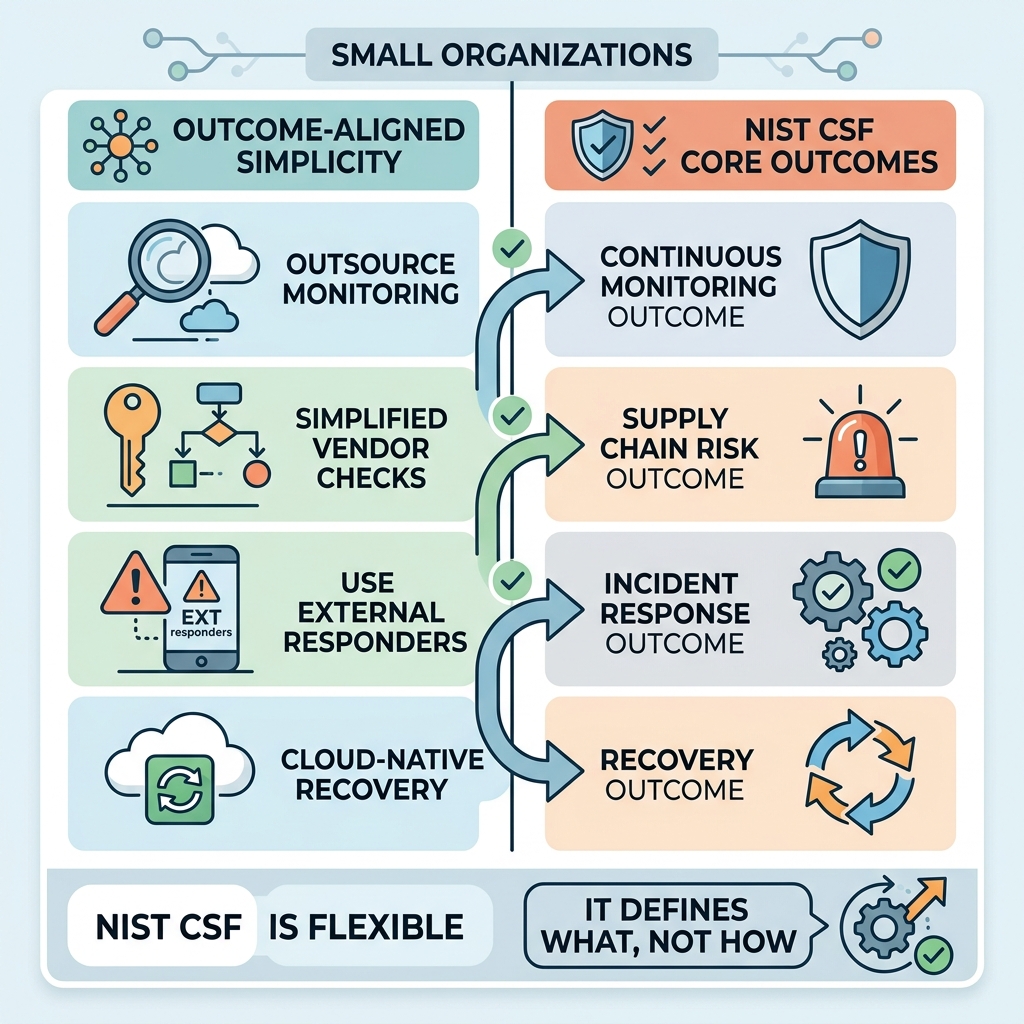
Every NIST CSF Outcome Applies — Even If You Implement It Differently
Read more: Every NIST CSF Outcome Applies — Even If You Implement It DifferentlySmall organizations often say, “That part of NIST CSF doesn’t apply to us.” But when you examine the outcomes, every one of them applies — even if the implementation looks different. For example: The outcome is the same. The method is different. NIST CSF is flexible by design. It defines what must be true…
-
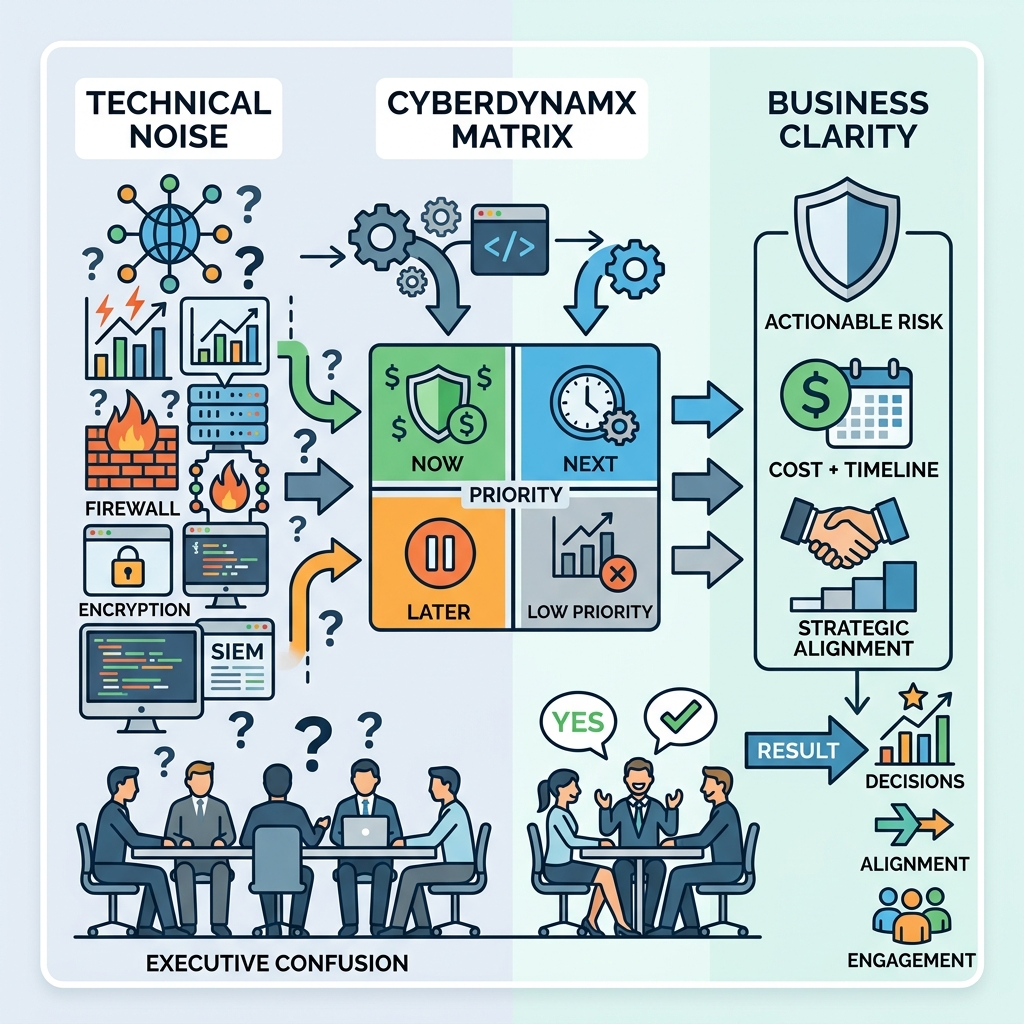
How to Communicate Cyber Risk Without Technical Jargon
Read more: How to Communicate Cyber Risk Without Technical JargonCybersecurity leaders often know exactly what the risks are — but struggle to communicate them in a way executives can act on. Technical jargon, tool‑centric explanations, and overly detailed descriptions create confusion instead of clarity. The truth is simple: Cyber risk must be communicated in business language. Executives don’t need to understand encryption algorithms,…

News & Updates
Buy my book
The Art and Science of Building a Simplified Digital Security Program
In CyberDynamX, I guide you through the process of creating a structured, resilient digital security program tailored to meet your organization’s unique needs. This approach helps integrate security seamlessly into daily operations, setting the foundation for a proactive cybersecurity culture.
- Master risk management and build a risk-aware culture.
- Classify and secure essential data assets.
- Design a governance framework with robust security architecture.
- Establish clear policies, standards, and control measures.
- Implement resilient strategies without relying on “quick fixes.”

If you’re looking for someone with that rare combination of character, vision and leadership, who can still roll up their sleeves to get things done, meet Curtis Blais.
President
SC Canada Services Inc.
He is a visionary…
CTO
ATB Financial
I have been consistently impressed by Curtis' professional competency and solid knowledge in the IT security, compliance and governance disciplines.
Sr. Manager
Alberta Blue Cross
…you speak with humility, something that makes you very approachable, especially to people who may not have the confidence of those more established in the field. Cybersecurity needs more people like you.
Chief Information Security Officer
University of Northern BC
Curtis is a pragmatic strategist who emphasizes risk reduction and digital resilience by implementing effective controls in key areas to thwart one's adversaries.
Field CTO Cybersecurity
Cisco Canada
Curtis is one of the most creative mind I know, and taught me to think outside of the box…
Senior Security Consultant
TELUS
Curtis is a strategic 21st Century thinker and doer and he has a vision that captures the imagination. Curtis is a highly regarded leader in the security community.
CSO / Canadian Security Director of the Year
TELUS
He always demonstrates professionalism in every facet of business and has a proven record of success as a leader…
Director, National Solutions Delivery
TELUS
I’ve had the privilege of working with Curtis on some really cool things this past year. He’s a trusted source, whip smart, super humble, and an all-around great guy. If you’re employed in any cyber security role regardless if you’re just starting out or have a few battle scars, his book is probably something you want to add to your library.
Director, Cybersecurity & CISO
MacEwan University
Your work has been sooo helpful!
Director, Information Technology
Olds College
I believe the book is well positioned to be a thought-leader and practical guide for organizations looking to establish a solid security posture. I love how the book transcends the commercial and not-for-profit sectors, and is applicable to companies in Canada, the US, and internationally. Highly recommended and worth every penny!
CISO
MRNET
I still have the materials and lessons learned from the leadership program you did for us!
Manager Server Infrastructure & Operations
Alberta Blue Cross
Curtis is a leader, humble, creative, and has a tremendous amount of integrity.
Team Manager
Alberta Blue Cross
I've never worked with a person with more integrity.
Information Security Analyst
AIMCo
I'm a practical person, and I don't like to fall into excessive praising, but I chose my words lightly when I say you were very inspiring.
Sr. Consultant/Manager
KPMG
Much of your work regarding IT Security Governance has remained as the foundation for effective operations. And it provided an excellent foundation that we could expand upon. Your great work, and its cumulative impacts, set us up for future success in a lot of regards. Also, our Enterprise Architect is a big fan.
Director of Information, Risk & Compliance
NorQuest College
Curtis has proven to be a strong and highly knowledgeable professional who has served our organization very well…
CIO
Alberta Blue Cross
I wish that I’d had this book when I was starting out in cyber security. It would have saved me from making many common and uncommon mistakes, leaving me free to find new and creative mistakes of my own to make.
Chief Information Security Officer
University of Northern BC
Curtis is the definition of professionalism. He is one of the most knowledgeable professionals it is my pleasure to know in the areas of Security and Compliance.
Curtis’ leadership and guidance in advancing cybersecurity programs within Canada’s higher education sector highlight his deep expertise in risk management and his commitment to high standards.
Chief Information Security Officer
British Columbia Institute of Technology